Soroban
Soroban Smart Contracts in Rust: Security Patterns and Pitfalls
Security patterns for Soroban contracts on Stellar, and the pitfalls that show up most in Rust code.
AI agents review every function, and OrCa fuzzes your code against the behavior you specify.
For Soroban smart contracts on Stellar. Tools refined through 150+ security audits.
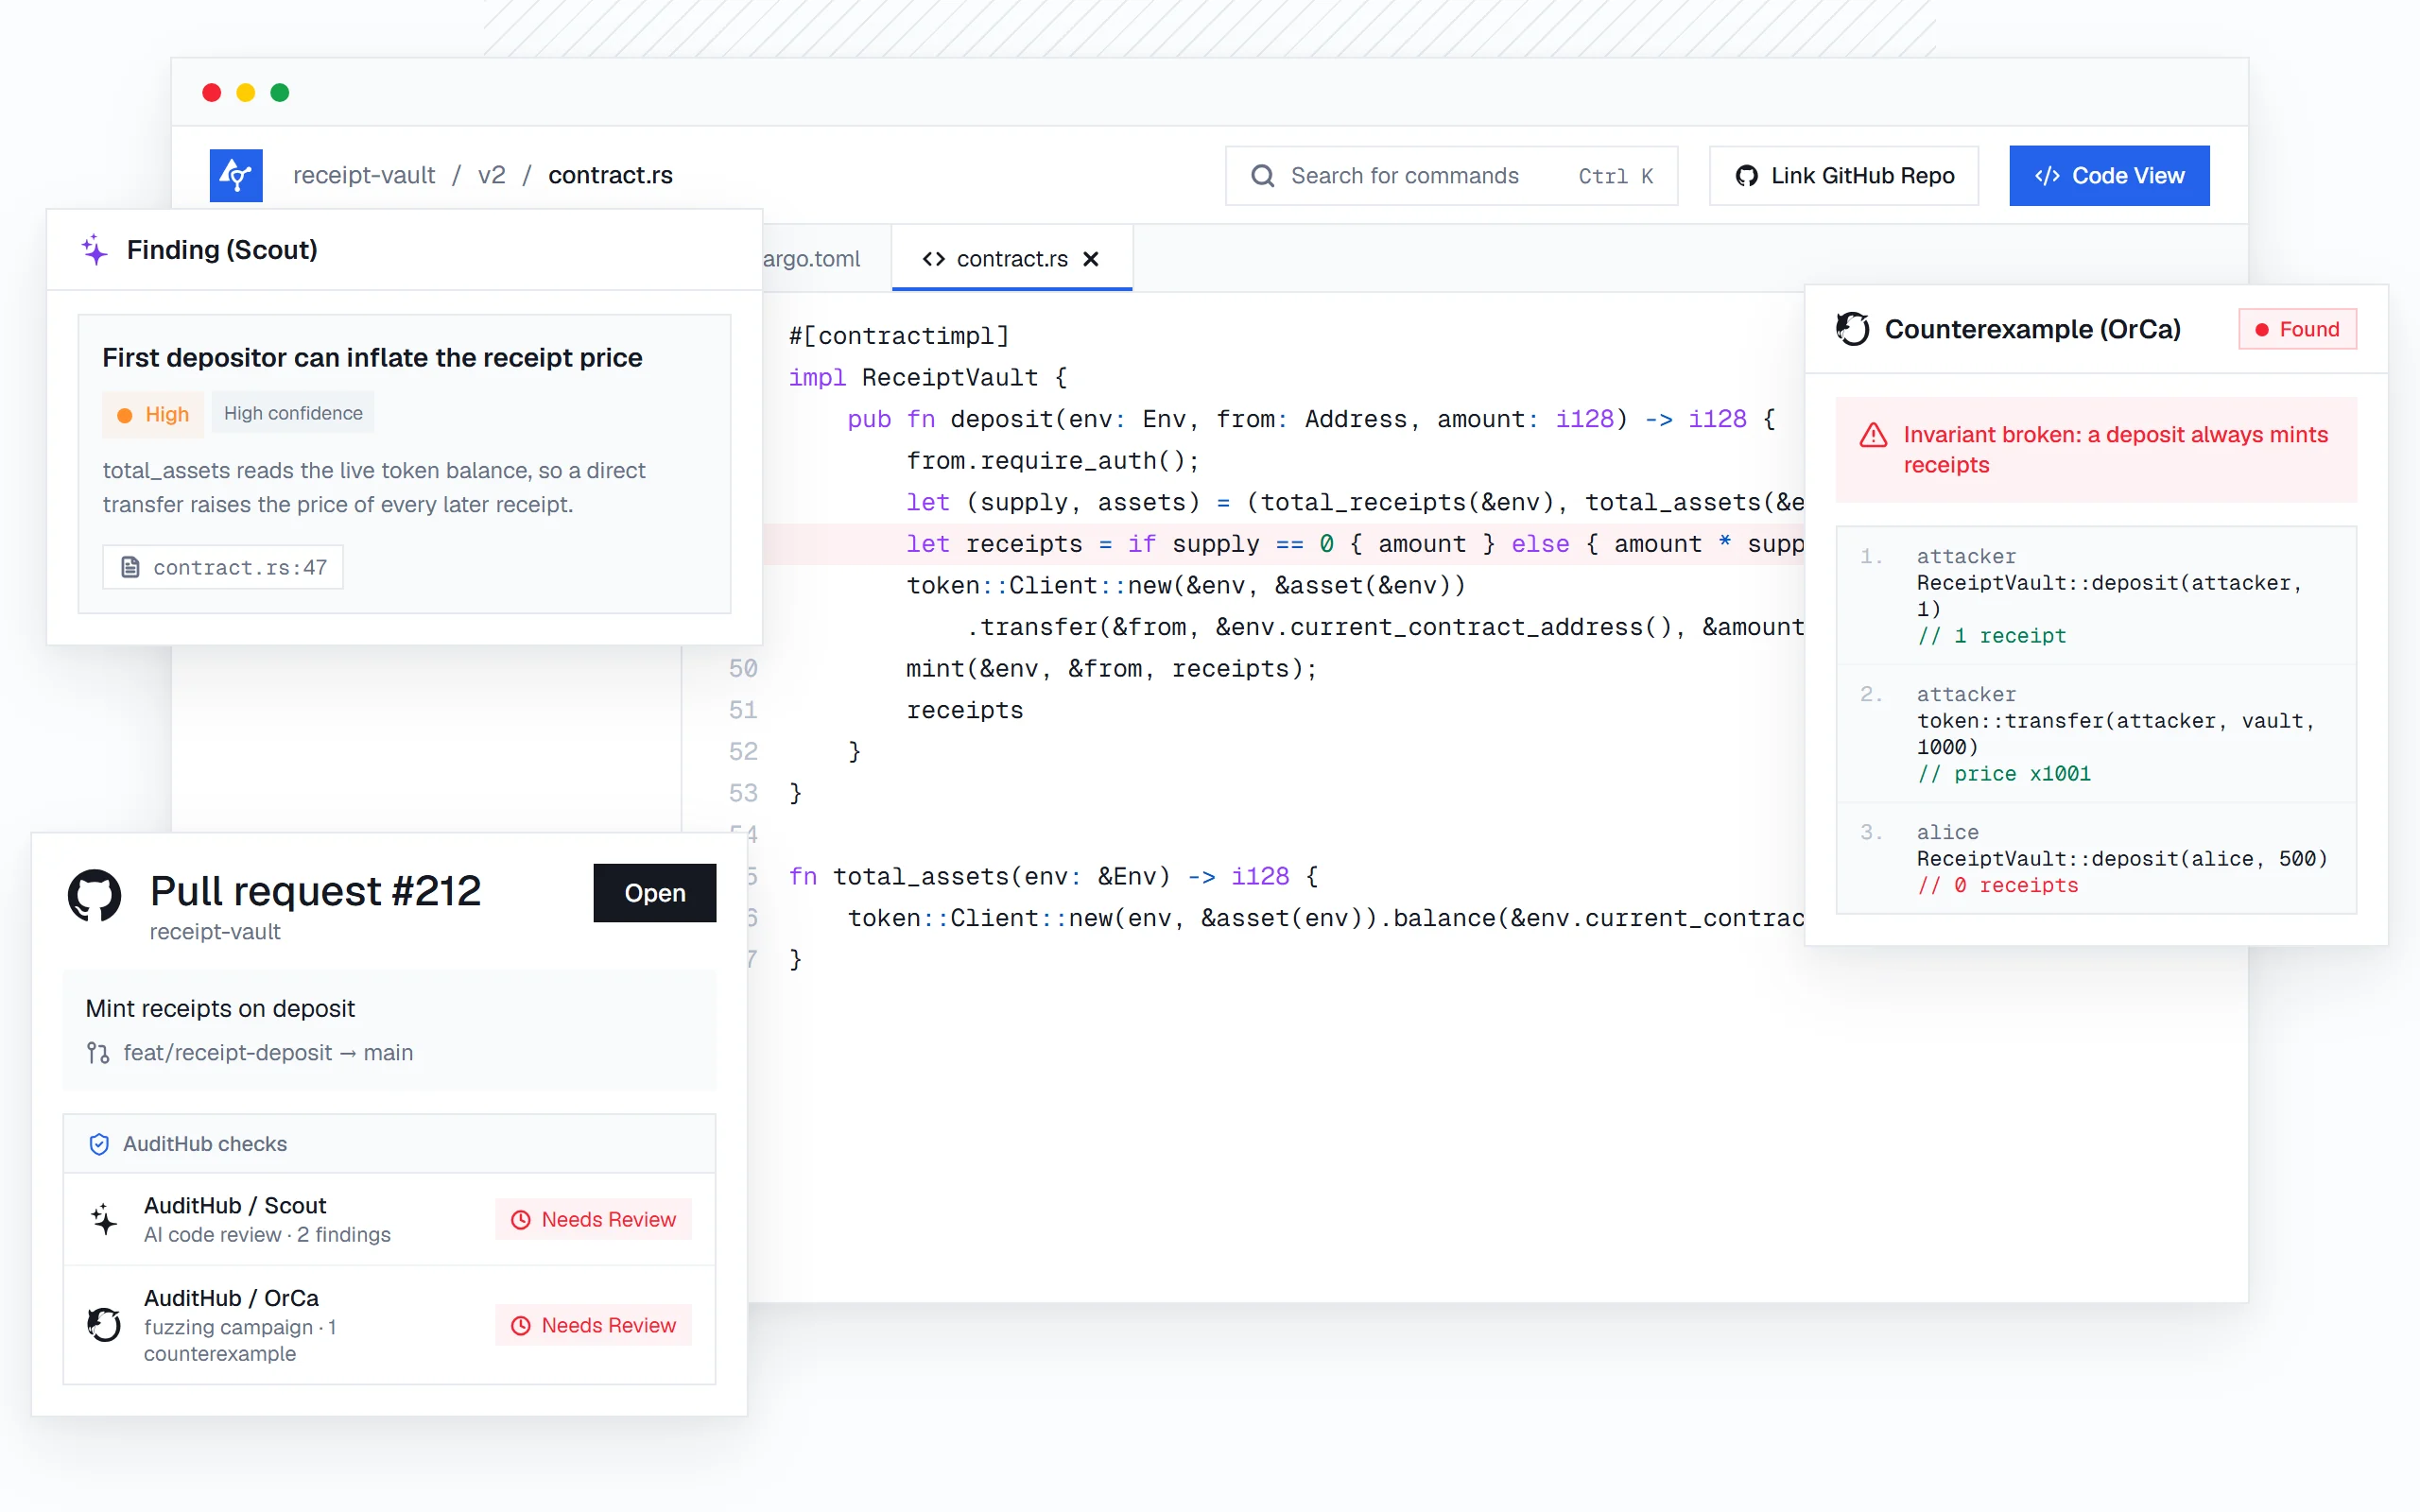
Scout learns your protocol, reviews every contract function, tests each finding with OrCa where a property applies, and remembers what it learned for the next run.
// 001
Models your contracts, storage and authorization rules.
// 002
Looks for exploitable bugs in every function.
// 003
Runs OrCa against the property at stake.
// 004
Keeps what it learned for the next run.
OrCa brings specification guided fuzzing, built on formal methods, to your Stellar contracts.
OrCa tests your Soroban contracts against the behavior you specify in [V], or against the existing specification library, and returns exact inputs and traces for every violation.
// SOROBAN
Explore OrCa →Soroban contracts are written in Rust. See how AuditHub covers Rust smart contracts.
Well-known risks in Stellar contracts. Scout reviews each one; OrCa tests the ones you can state as a property.
| Vulnerability | What happens | Covered by |
|---|---|---|
| Missing authorization | A function that moves funds or changes state without requiring auth from the right address. | Scout, OrCa |
| Storage expiry | Entries whose time to live is never extended: persistent data gets archived, temporary data is deleted. | Scout |
| Arithmetic errors | Token math on i128 without checked operations, or rounding that leaks value. | Scout, OrCa |
| Unprotected upgrades | A contract upgrade that anyone, or the wrong admin, can trigger. | Scout, OrCa |
| Untrusted contract addresses | A token or contract address passed in by the caller and never validated. | Scout |
| Broken invariants | Balance, supply or reserve rules that stop holding. | OrCa |
Scout flags a transfer function that never requires auth from the sender. OrCa tests the rule you specified, that only an owner can move their balance, and returns the evidence: the exact call and inputs that break it.
Scout AI - Findings
Line 75
First depositor can inflate the share price
OrCa - Evidence
Share price manipulation reproduced
The exact inputs and the trace that break the expected behavior.
// COUNTEREXAMPLE FOUND
Keep writing contracts with the Soroban SDK and building with cargo and the Stellar CLI. Connect your GitHub repository and run checks in GitHub Actions on every commit.
Building Soroban contracts with a coding agent? Run OrCa through AuditHub MCP.
AuditHub checks your Soroban code on every change, so your auditors start from a cleaner baseline and spend their time on design and logic. The audit still gives you a signed expert review.
Before audit
During audit
After audit
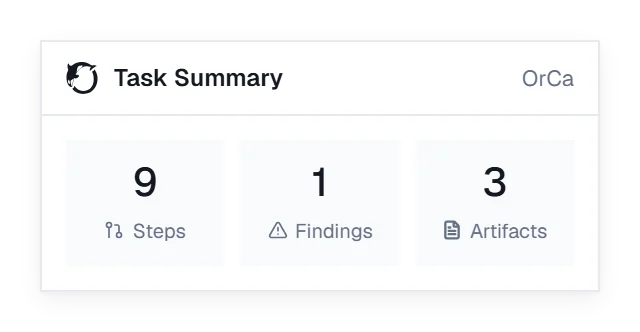
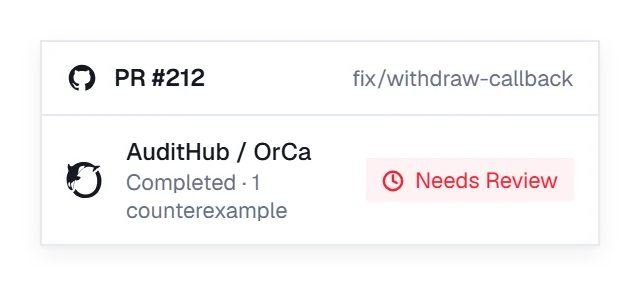
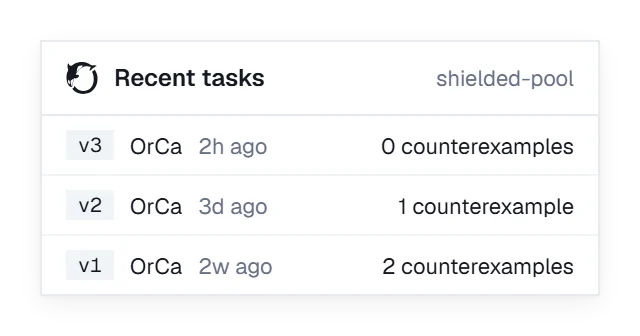
OrCa was built by the Veridise auditors behind AuditHub, from the way they test contracts in real engagements.
An expert review of your Stellar smart contracts for flaws such as missing authorization, storage expiry and arithmetic errors before deployment. AuditHub adds continuous checks between audits: AI agents review every function and OrCa tests it against your specification.
Yes. AI agents review your Soroban code and OrCa fuzzes it against the behavior you specify.
Any behavior you can state as a property: who may call a function, how balances and supply must change, who may upgrade the contract. Scout’s review covers the rest, such as storage expiry.
You can write your own in [V], or start from the existing specification library.
No. It checks every change between audits, and the audit gives you a signed expert review.
Still have questions? Contact us
Soroban
Security patterns for Soroban contracts on Stellar, and the pitfalls that show up most in Rust code.
Rust Security
Common bugs in Rust smart contracts and how static analysis catches them before deployment.
Security Tools
What static analysis, fuzzing and formal proofs each catch, and how they fit together in one workflow.
Start reviewing and fuzzing your Stellar contracts today.