Static analysis
Catches critical bugs across contract boundaries.
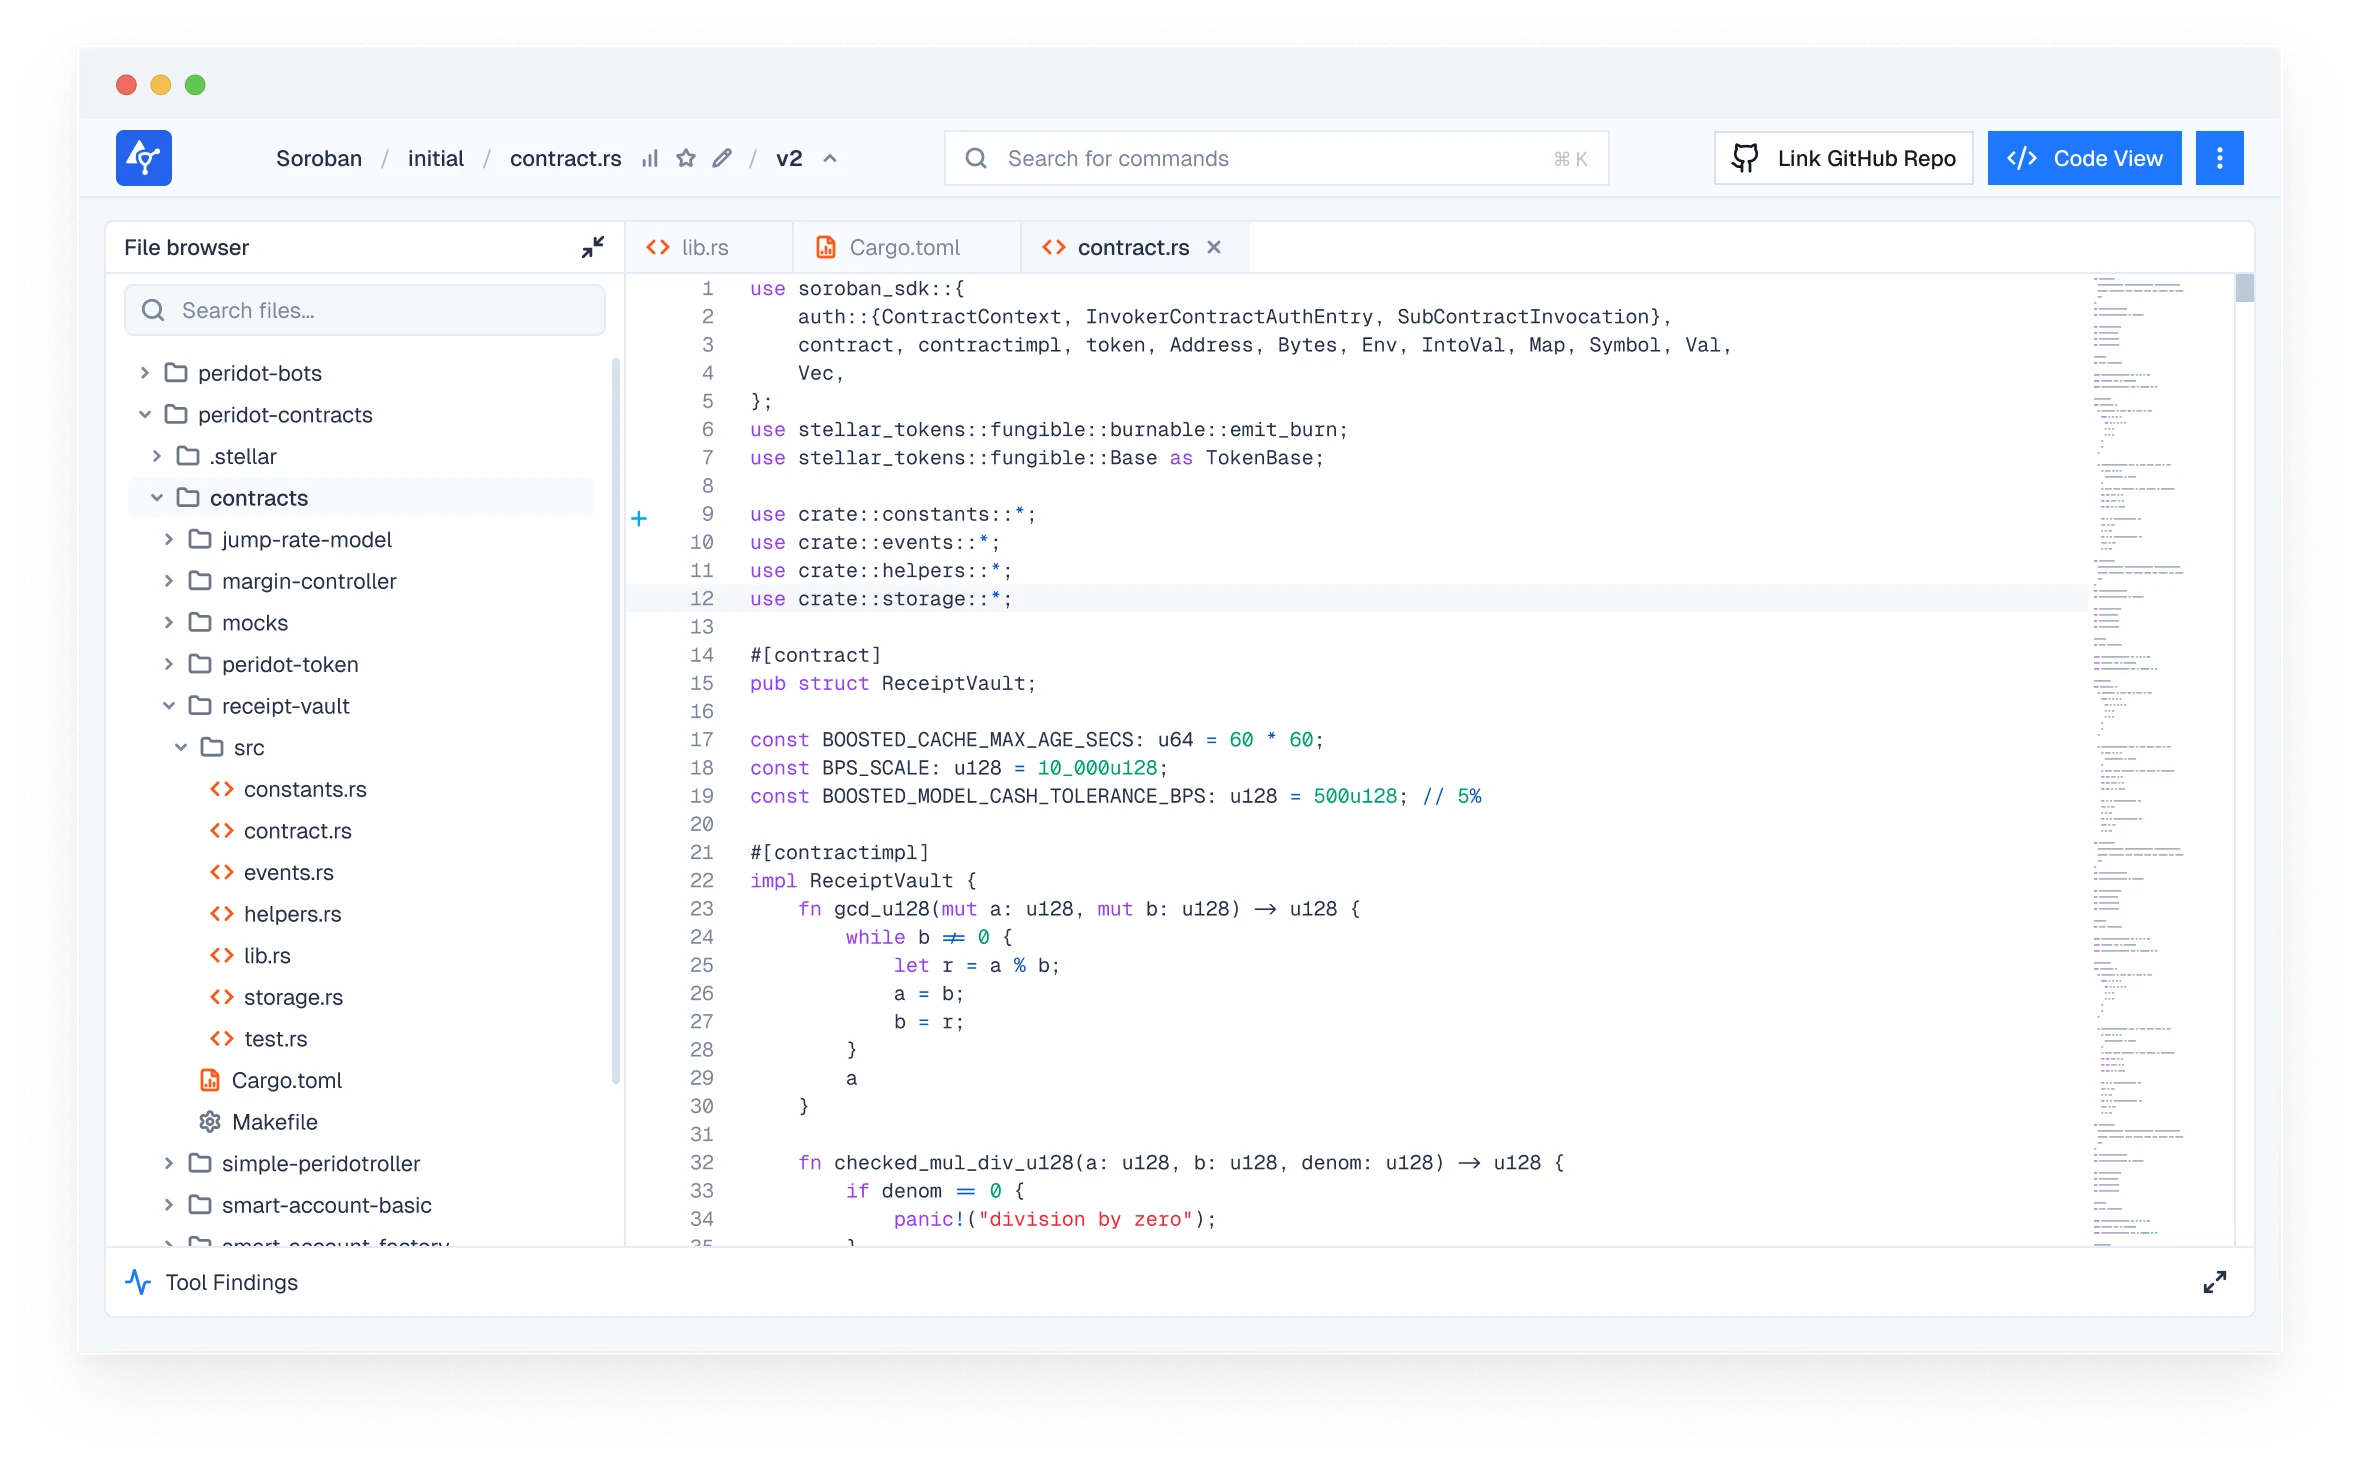
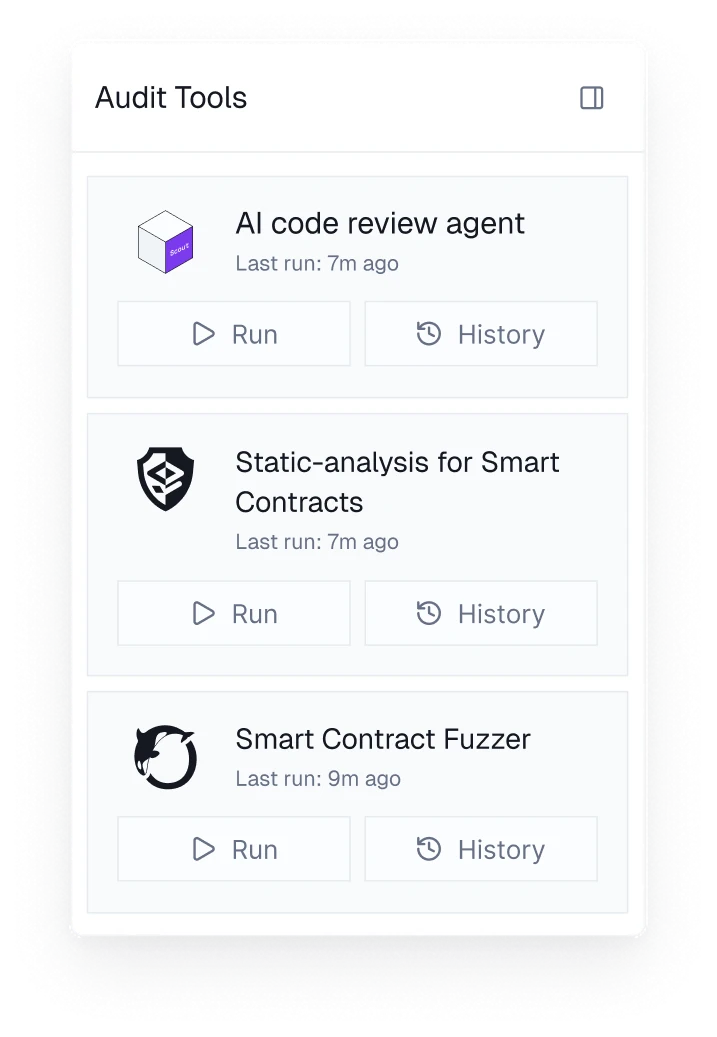
Built on formal methods. AI agents review every change to your code, and four security tools check what they find, so nothing ships unchecked after your audit.
TRUSTED BY
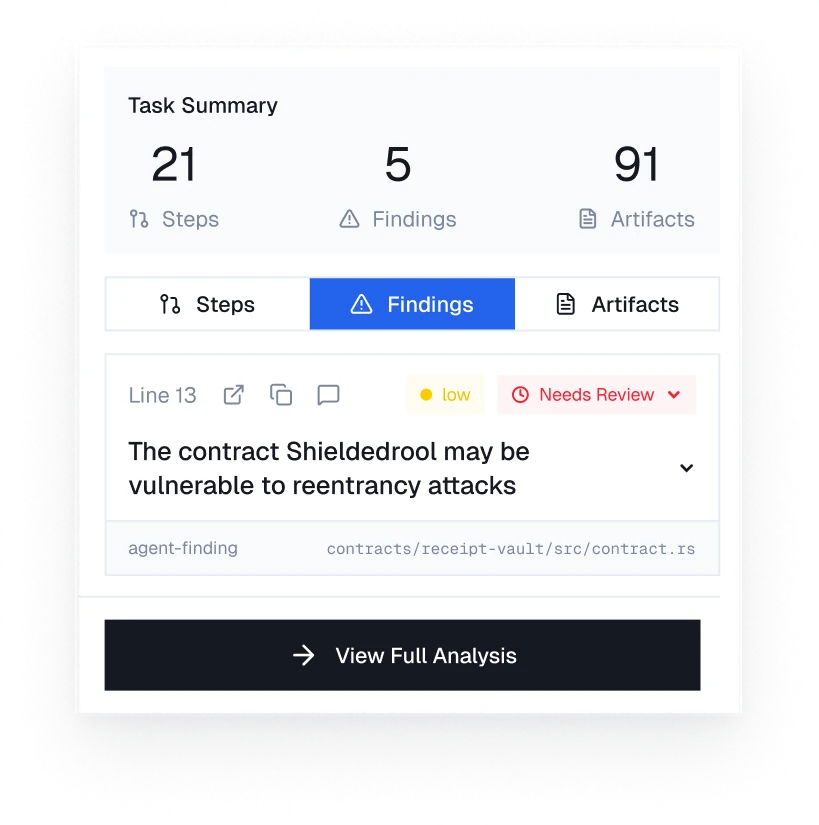
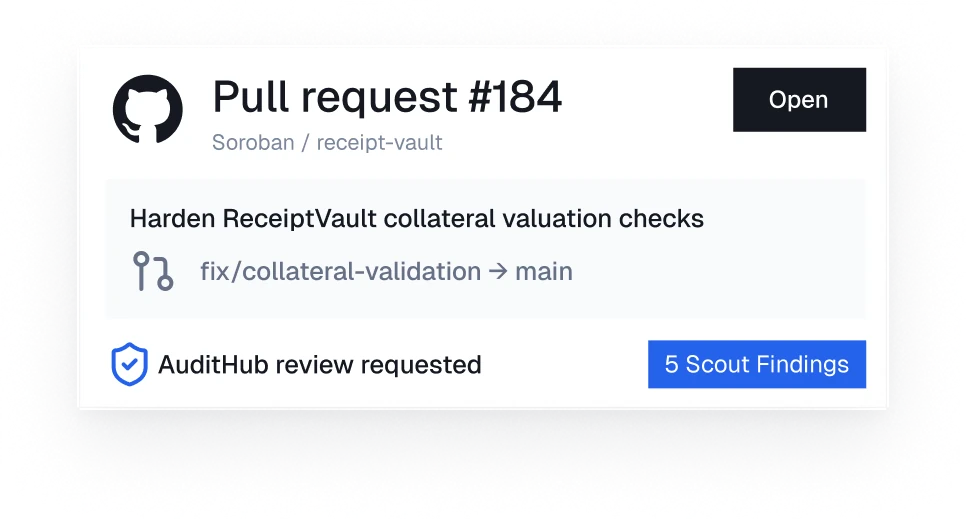
Scout learns your protocol, hunts for exploitable bugs, tests each one with the right security tool, and remembers what it learned for the next run.
Builds a threat model and the invariants your protocol should hold.
// BUILD THE MODELLooks for exploitable paths, the way a security researcher would.
// TRACE THE PATHSends each suspect to the right tool: Vanguard, OrCa, ZK Vanguard or Picus.
// VERIFY WITH TOOLSKeeps what it learned, including your corrections, for the next run.
// CARRY CONTEXT FORWARDCorrections and findings are stored and used to improve the next run
Use Scout directly in AuditHub, or bring AuditHub's security tools into your own coding agent through MCP. Same tools, same results, choose the experience that fits your workflow.
Run Scout directly in AuditHub to analyze your code, investigate findings, and retain context across runs.
Bring AuditHub's security tools into your coding agent, right where you write and review code.
Scout reports a suspected bug in plain terms. The right tool checks it and returns the evidence: a call graph, an exact transaction trace or a counterexample.
Scout AI - Findings
Line 75
First depositor can inflate the share price
When total_shares == 0, the first depositor receives shares 1:1 with deposited assets, allowing share price manipulation.
AuditHub - Evidence
Share price manipulation reproduced
A concrete transaction sequence breaks the share-price invariant.
// COUNTEREXAMPLE FOUND
Catches critical bugs across contract boundaries.
Tests your contracts against your [V] specs and returns the transactions that break them.
Catches likely underconstrained signals.
Proves your circuits are deterministic, or returns a counterexample.
For smart contracts and ZK circuits in Solidity, Rust, Soroban, Circom, Halo2 and Plonky3.
Explore the security toolsFrom solo developers to security teams, AuditHub makes advanced security workflows accessible without adding complexity.
Run Scout and AuditHub’s security tools on your code. Find vulnerabilities, review the evidence, and strengthen your contracts as you build.
Bring your team together in AuditHub to analyze complex protocols. Review findings, verify fixes, and keep everyone aligned on the evidence.
From infrastructure to applications, see how teams use AuditHub to find critical issues, strengthen their code, and ship with confidence.
21/26
circuits proven deterministic
How Matter Labs used AuditHub’s Picus to prove determinism across most of ZKsync Airbender’s circuits, in an engagement that...
6
security issues found and fixed
A line-by-line review of Mina Multisig’s FROST integration found six issues before Nori’s first production deployment on Mina.
Every plan includes AuditHub’s four security tools. Choose the credits, projects, seats, and Scout capabilities that fit your needs.
Trying AuditHub with no commitment.
Light monthly use for solo security work.
$79/month
See detailed pricingRegular security checks by a small team.
$279/month
See detailed pricingSubstantial monthly security use by a dedicated security team.
$899/month
See detailed pricingRigorous security checks for large or regulated organizations.
Custom
Contact UsExplore credits, Scout features, integrations, seats, and project limits to find the right plan for you.
Everything you need to know about AuditHub, its security tools, and how they fit into your workflow.
Software that checks smart contracts and ZK circuits for vulnerabilities. On AuditHub, AI agents review your code and four security tools built on formal methods check what they find.
A security tool checks each AI finding before you act on it. Related findings are grouped, and marking a root cause clears linked false alarms in bulk.
No. AuditHub checks your code on every change, and your audit still gives you a signed expert review.
Yes. AuditHub MCP lets your coding agent call the security tools during the session.
Only the people you add to your organization see it, and it never trains a model.
Still have questions? Contact us
Stay ahead of emerging Web3 vulnerabilities with research-backed insights from the AuditHub team.
Arcadia lost $3.5M to a call it let its caller shape. How a custom static detector catches that pattern..
External audits reveal critical vulnerabilities when your protocol is feature complete and ready to ...
How the AuditHub Approach Would Have Flagged Future Protocol’s $4.6M Bug: Pre-Mortem..