Solidity Security
Solidity Security: 12 Practices That Prevent Common Bugs
Twelve practices for Solidity code, from access control to external calls, with the bugs each one prevents.
AI agents review every contract. Vanguard runs static analysis and OrCa fuzzes against your specification, alongside your audit.
For Foundry and Hardhat projects. Static analysis and fuzzing shaped on 150+ security audits.
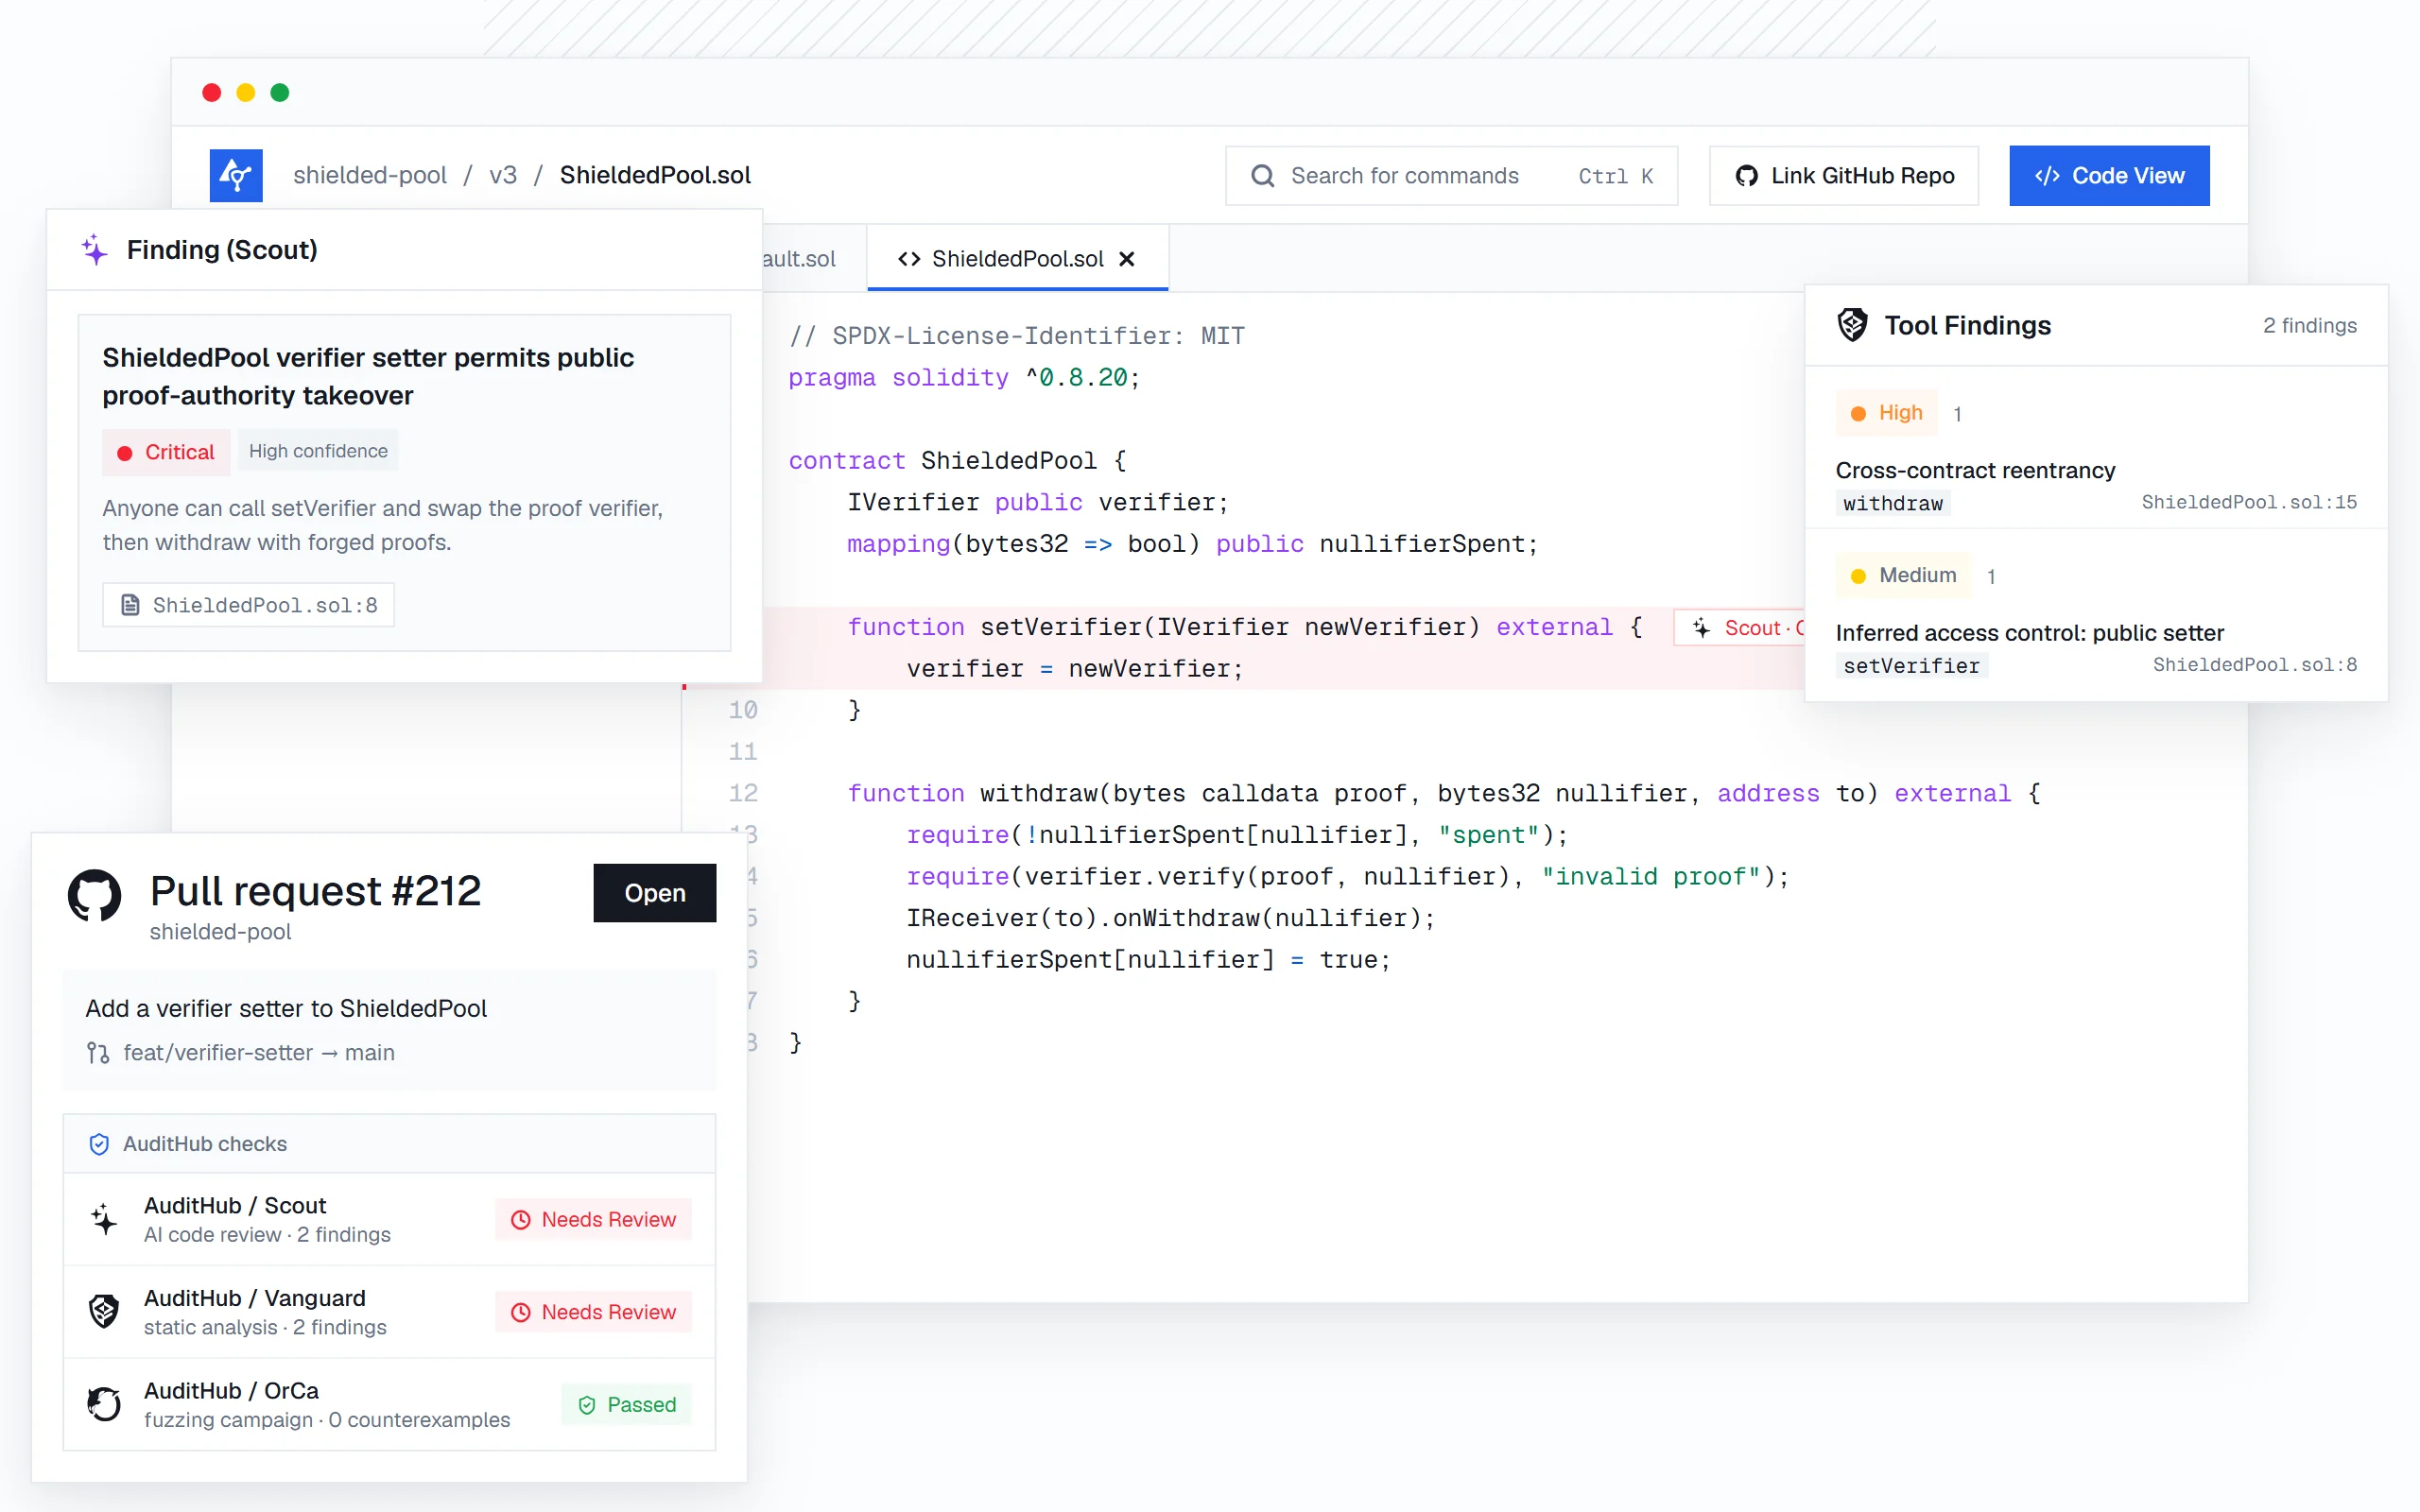
Scout learns your protocol, hunts for exploitable bugs across your contracts, tests each one with Vanguard or OrCa, and remembers what it learned for the next run.
// 001
Models your contracts, roles and value flows.
// 002
Looks for exploitable bugs, not style issues.
// 003
Runs Vanguard or OrCa on each finding.
// 004
Keeps what it learned for the next run.
Two security tools built on formal methods, run in sequence: Vanguard for breadth, OrCa for depth.
Vanguard detects reentrancy, unchecked return values and precision loss across contract boundaries, using abstract interpretation.
// SOLIDITY
Explore Vanguard →OrCa tests your contracts against the behavior you specify in [V], or against the existing specification library, and returns exact inputs and traces for every violation.
// SOLIDITY
Explore OrCa →Well-known Solidity bug classes, each mapped to the tool that catches or tests it.
| Vulnerability | What happens | Tool |
|---|---|---|
| Reentrancy | Including cross-contract and read-only reentrancy through shared storage. | Vanguard detects it; OrCa builds reentrancy attacks to test it. |
| Unchecked return values | External calls whose result is never validated. | Vanguard |
| Precision loss | Division before multiplication that silently drops value. | Vanguard |
| Flash loan manipulation | Logic an attacker can exploit by borrowing and repaying within one transaction. | Vanguard |
| Access control gaps | Functions callable by the wrong role. | Vanguard reports inferred access controls for review; OrCa tests the access rules you specify. |
| Broken invariants | Accounting, supply or share price rules that stop holding. | OrCa |
Scout flags a withdrawal path that may let a user leave with more than their share. OrCa tests the property you specified and returns the evidence: the exact transaction sequence and inputs that break it.
Scout AI - Findings
Line 142
First depositor can inflate the share price
OrCa - Evidence
Share price manipulation reproduced
The exact inputs and the trace that break the expected behavior.
// COUNTEREXAMPLE FOUND
Connect your repository and keep building with Foundry or Hardhat; Vanguard supports Solidity 0.8.4 and newer. Both tools run in GitHub Actions on every commit, so findings arrive during development.
Working with a coding agent? Run Vanguard and OrCa from your session through AuditHub MCP.
AuditHub checks your Solidity code on every change, so your auditors start on cleaner contracts and spend their time on design and logic. The audit still gives you a signed expert review.
Before audit
During audit
After audit
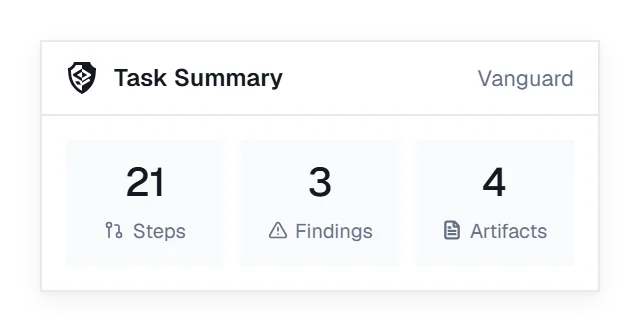
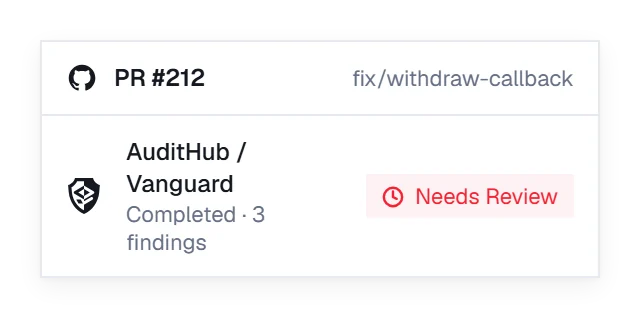
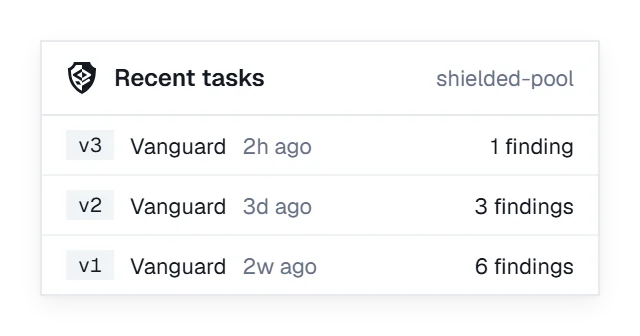
Vanguard and OrCa were shaped on real engagements by the Veridise auditors behind AuditHub.
An expert review of your contracts for vulnerabilities before deployment. AuditHub adds continuous checks between audits: AI agents review the code, and Vanguard and OrCa back each finding with evidence.
Vanguard supports Solidity 0.8.4 and newer on Foundry and Hardhat projects. OrCa works with Foundry and with Hardhat 2 and 3.
You can write your own in [V], or start from the existing specification library.
Vanguard detects vulnerability patterns by static analysis, without running your code. OrCa tests how your contracts behave against the properties you specify and returns the exact inputs that break them.
No. It checks every change between audits, and the audit gives you a signed expert review.
Still have questions? Contact us
Solidity Security
Twelve practices for Solidity code, from access control to external calls, with the bugs each one prevents.
Solidity Scanners
How static analysis reads your Solidity code, which bug classes it catches, and where it stops.
Fuzzing
How fuzzers and invariant tests work on smart contracts, and how to write properties that find real bugs.
Run Vanguard and OrCa on your contracts today.