Smart Contract Security
Smart Contract Security: Risks, Controls and How to Verify Code
The main risks in smart contracts, the controls that reduce them, and how to check that your code really holds.
AI agents and four formal methods tools for smart contracts and ZK circuits, on every plan. Start at no cost, then add seats and projects up to Enterprise.
TRUSTED BY
AI agents to review your code, security tools to check what they find, in one place.
Reviews your whole protocol and backs each finding with a security tool.
AI review agent
Explore Scout →Brings the security tools into your own coding agent.
Open Source MCP
Explore AuditHub MCP →Compare reviewing on the platform with reviewing from your coding agent.
Two ways to use AI
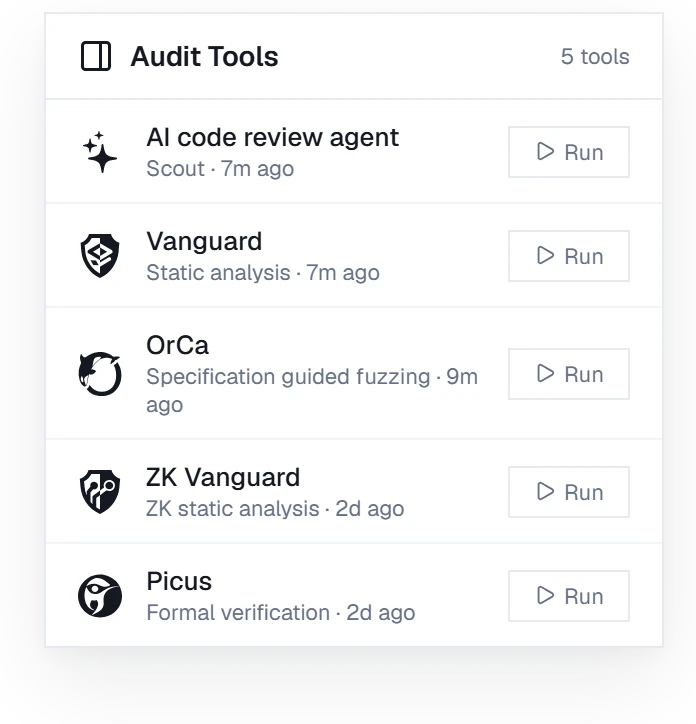
Explore AI code security →Vanguard, OrCa, ZK Vanguard and Picus, built on formal methods.
Four tools
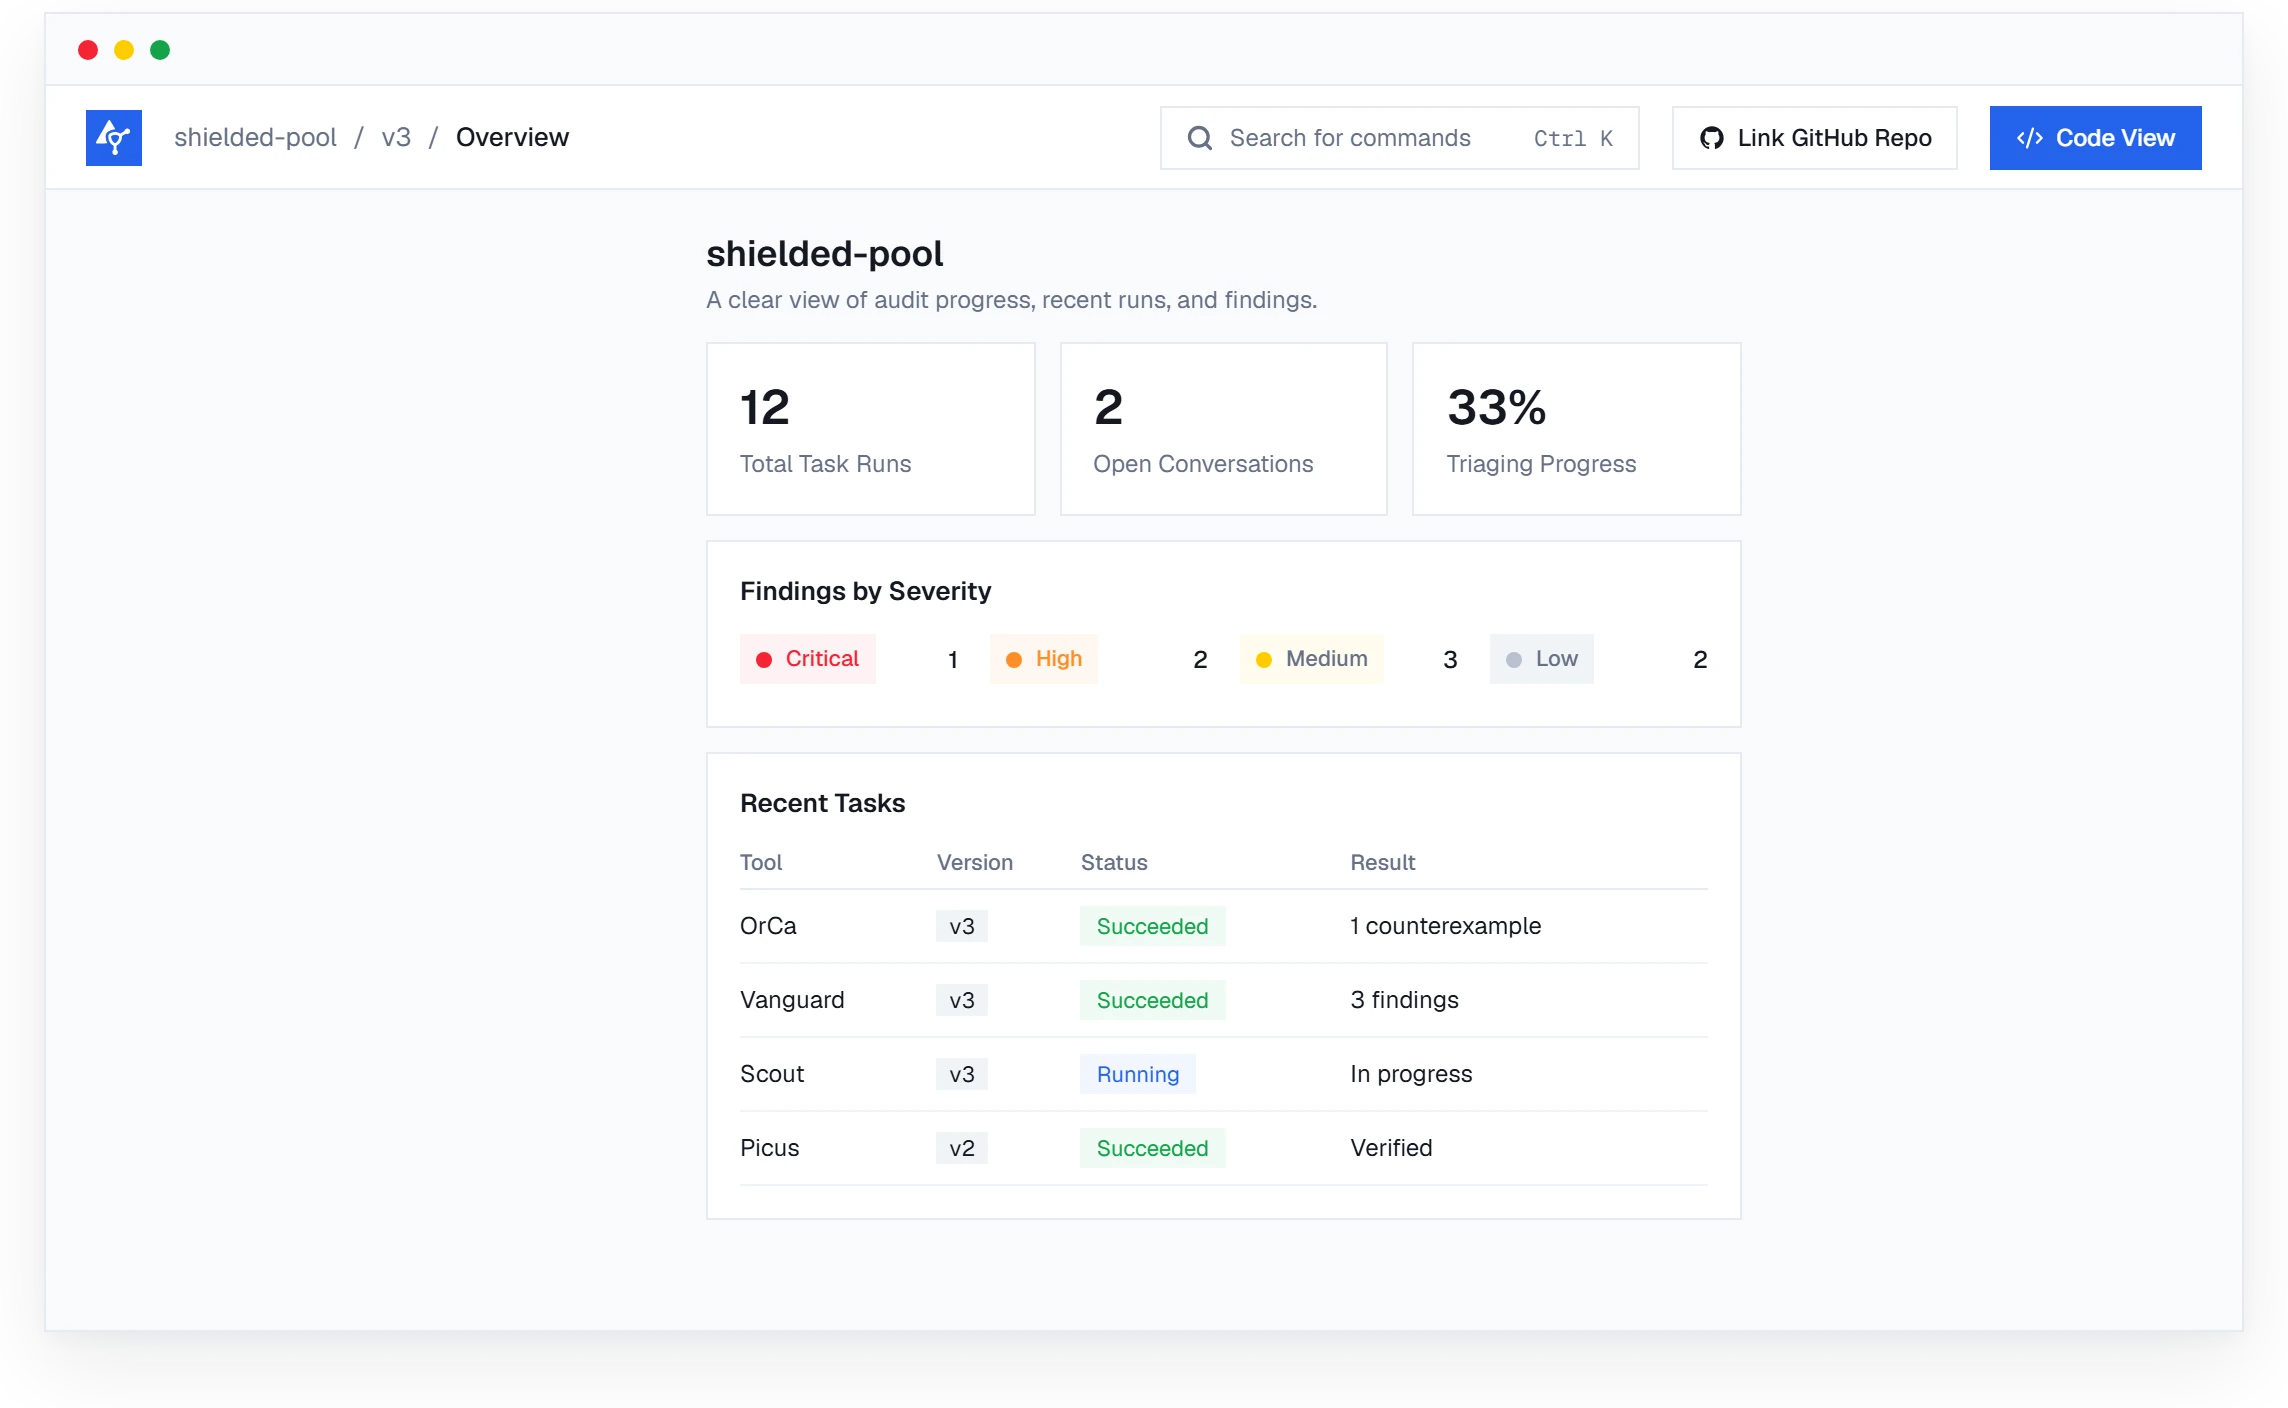
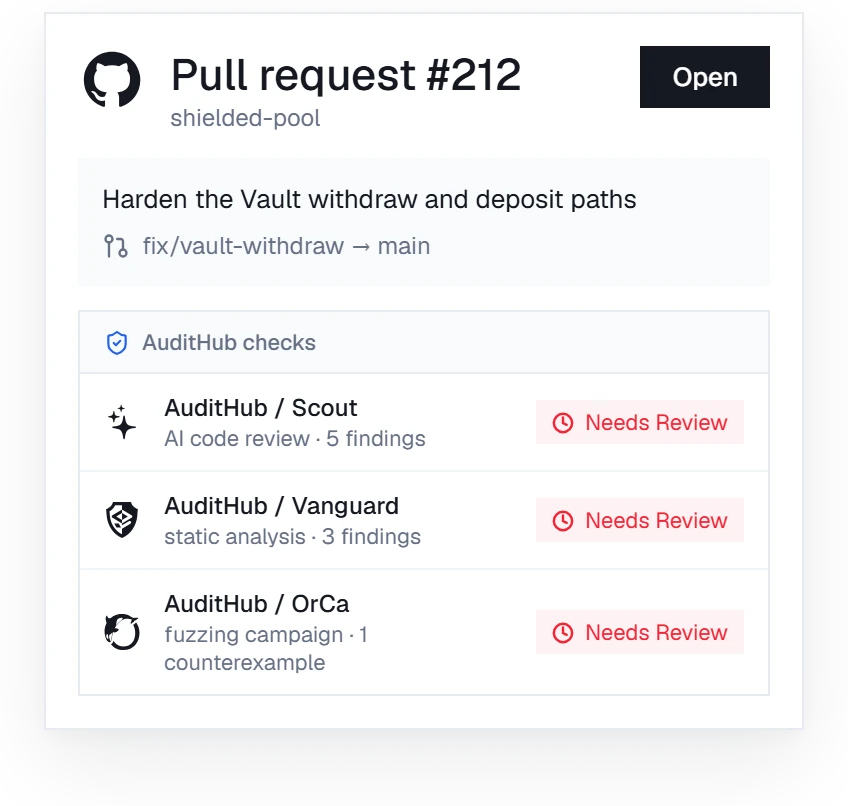
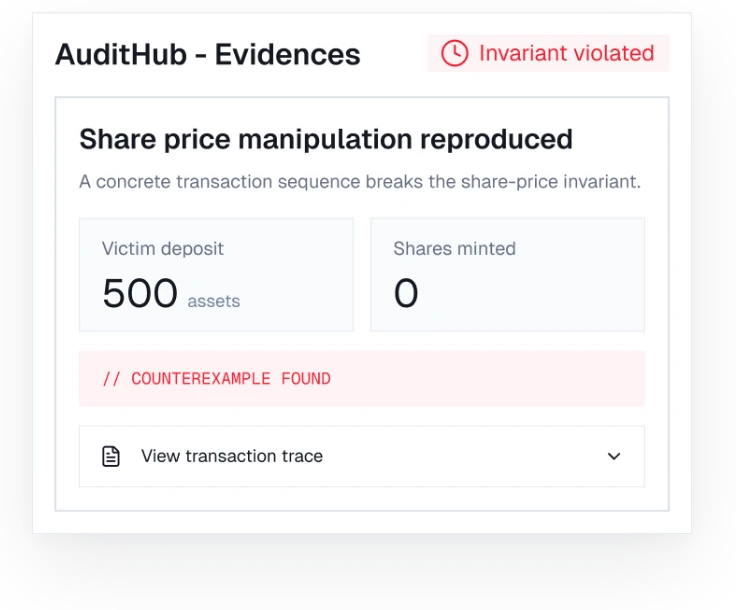
Explore Security tools →The agents find and report; the security tools check each finding and return evidence. Everything runs on your GitHub repository and in GitHub Actions, on every commit.
// 001
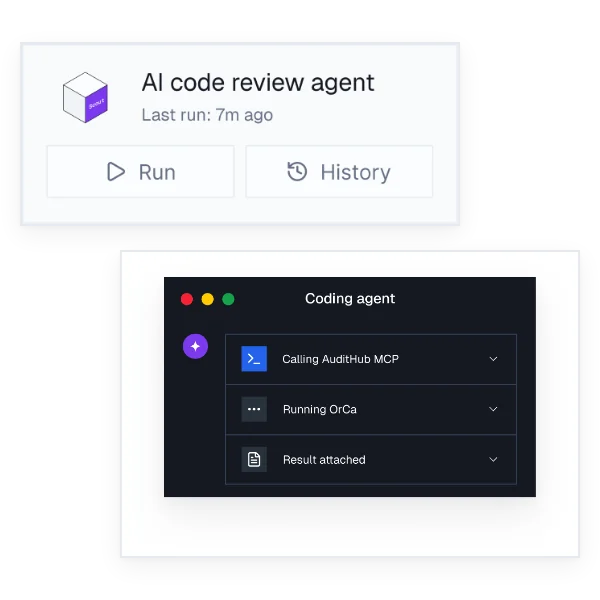
Scout, or your coding agent through AuditHub MCP
// 002
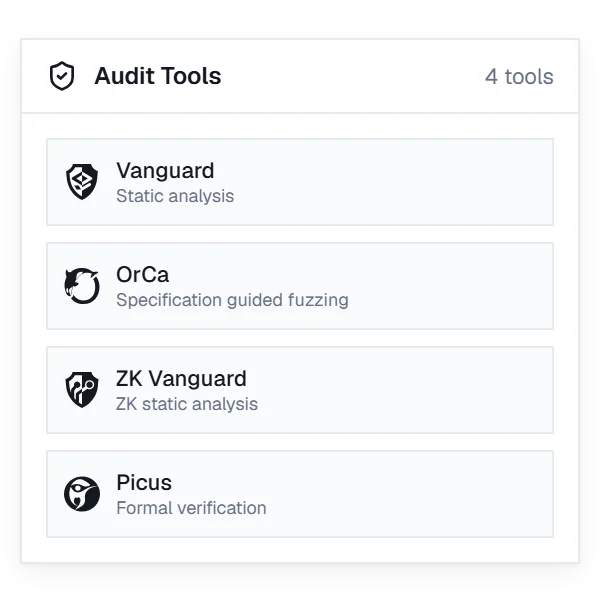
Vanguard, OrCa, ZK Vanguard, Picus
// 003
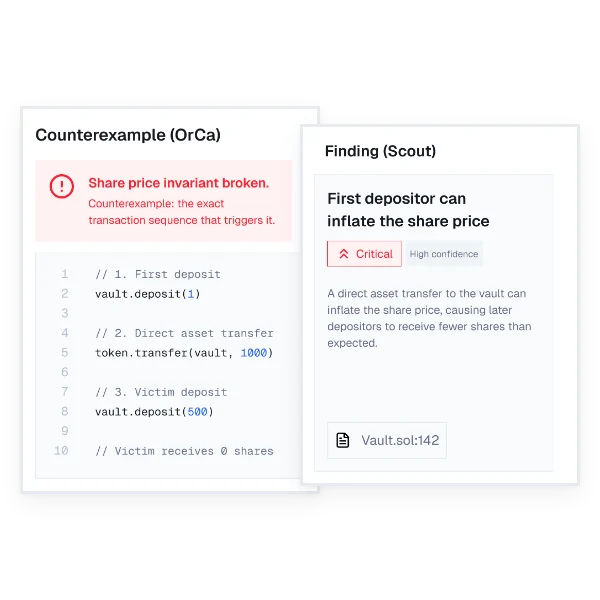
Call graphs, traces, proofs, counterexamples
Start from what you want to do, and go straight to the product built for it.
Start on Free, then add seats and projects as your team grows, up to Enterprise. Every plan, Free included, runs the same four tools at full strength.
Write custom detectors once and share them across your organization.
Mark a root cause once and related false alarms clear in bulk.
The tools run in GitHub Actions, so issues surface during development.
Add seats and projects as your team grows. Plans differ in credits, seats, projects and AI agent features, never in security tools.
// 001
Trying AuditHub with no commitment.
// 002
Light monthly use for solo security work.
$79/month
Start for Free Now// 003
Regular security checks by a small team.
$279/month
Start for Free Now// 004
Substantial monthly security use by a dedicated security team.
$899/month
Start for Free Now// 005
Rigorous security checks for large or regulated organizations.
Custom
Contact UsCredits, seats, projects and Scout features, side by side.
RISC Zero runs Picus in CI on its zkVM and caught 35 issues during development. The tools were shaped on 150+ security audits by the Veridise auditors behind AuditHub.
It brings the checks your code needs into one place, from review to evidence. AuditHub combines AI agents with four security tools built on formal methods, for smart contracts and ZK circuits.
Yes. The Free plan comes with free credits and all four security tools at full strength. Paid plans add seats and projects as your team grows.
Scout, or your own coding agent through AuditHub MCP, finds and reports suspected bugs. Vanguard, OrCa, ZK Vanguard and Picus check them and return evidence.
It connects to your GitHub repository and runs in GitHub Actions on every commit. Solidity projects build with Foundry or Hardhat.
No. It checks your code continuously, so your audit starts on cleaner code and focuses on design and logic. The audit still gives you a signed expert review.
Still have questions? Contact us
Smart Contract Security
The main risks in smart contracts, the controls that reduce them, and how to check that your code really holds.
Security Tools
What static analysis, fuzzing and formal proofs each catch, and how they fit together in one workflow.
AI Code Review
How AI agents review smart contract code, what they miss on their own, and why findings need tool evidence.
Connect a repository and run all four security tools today.