The smart contract fuzzer that exposes deep bugs across contracts

Describe the expected behavior in [V] specifications. OrCa generates thousands of test cases and returns exact inputs and traces for every violation.
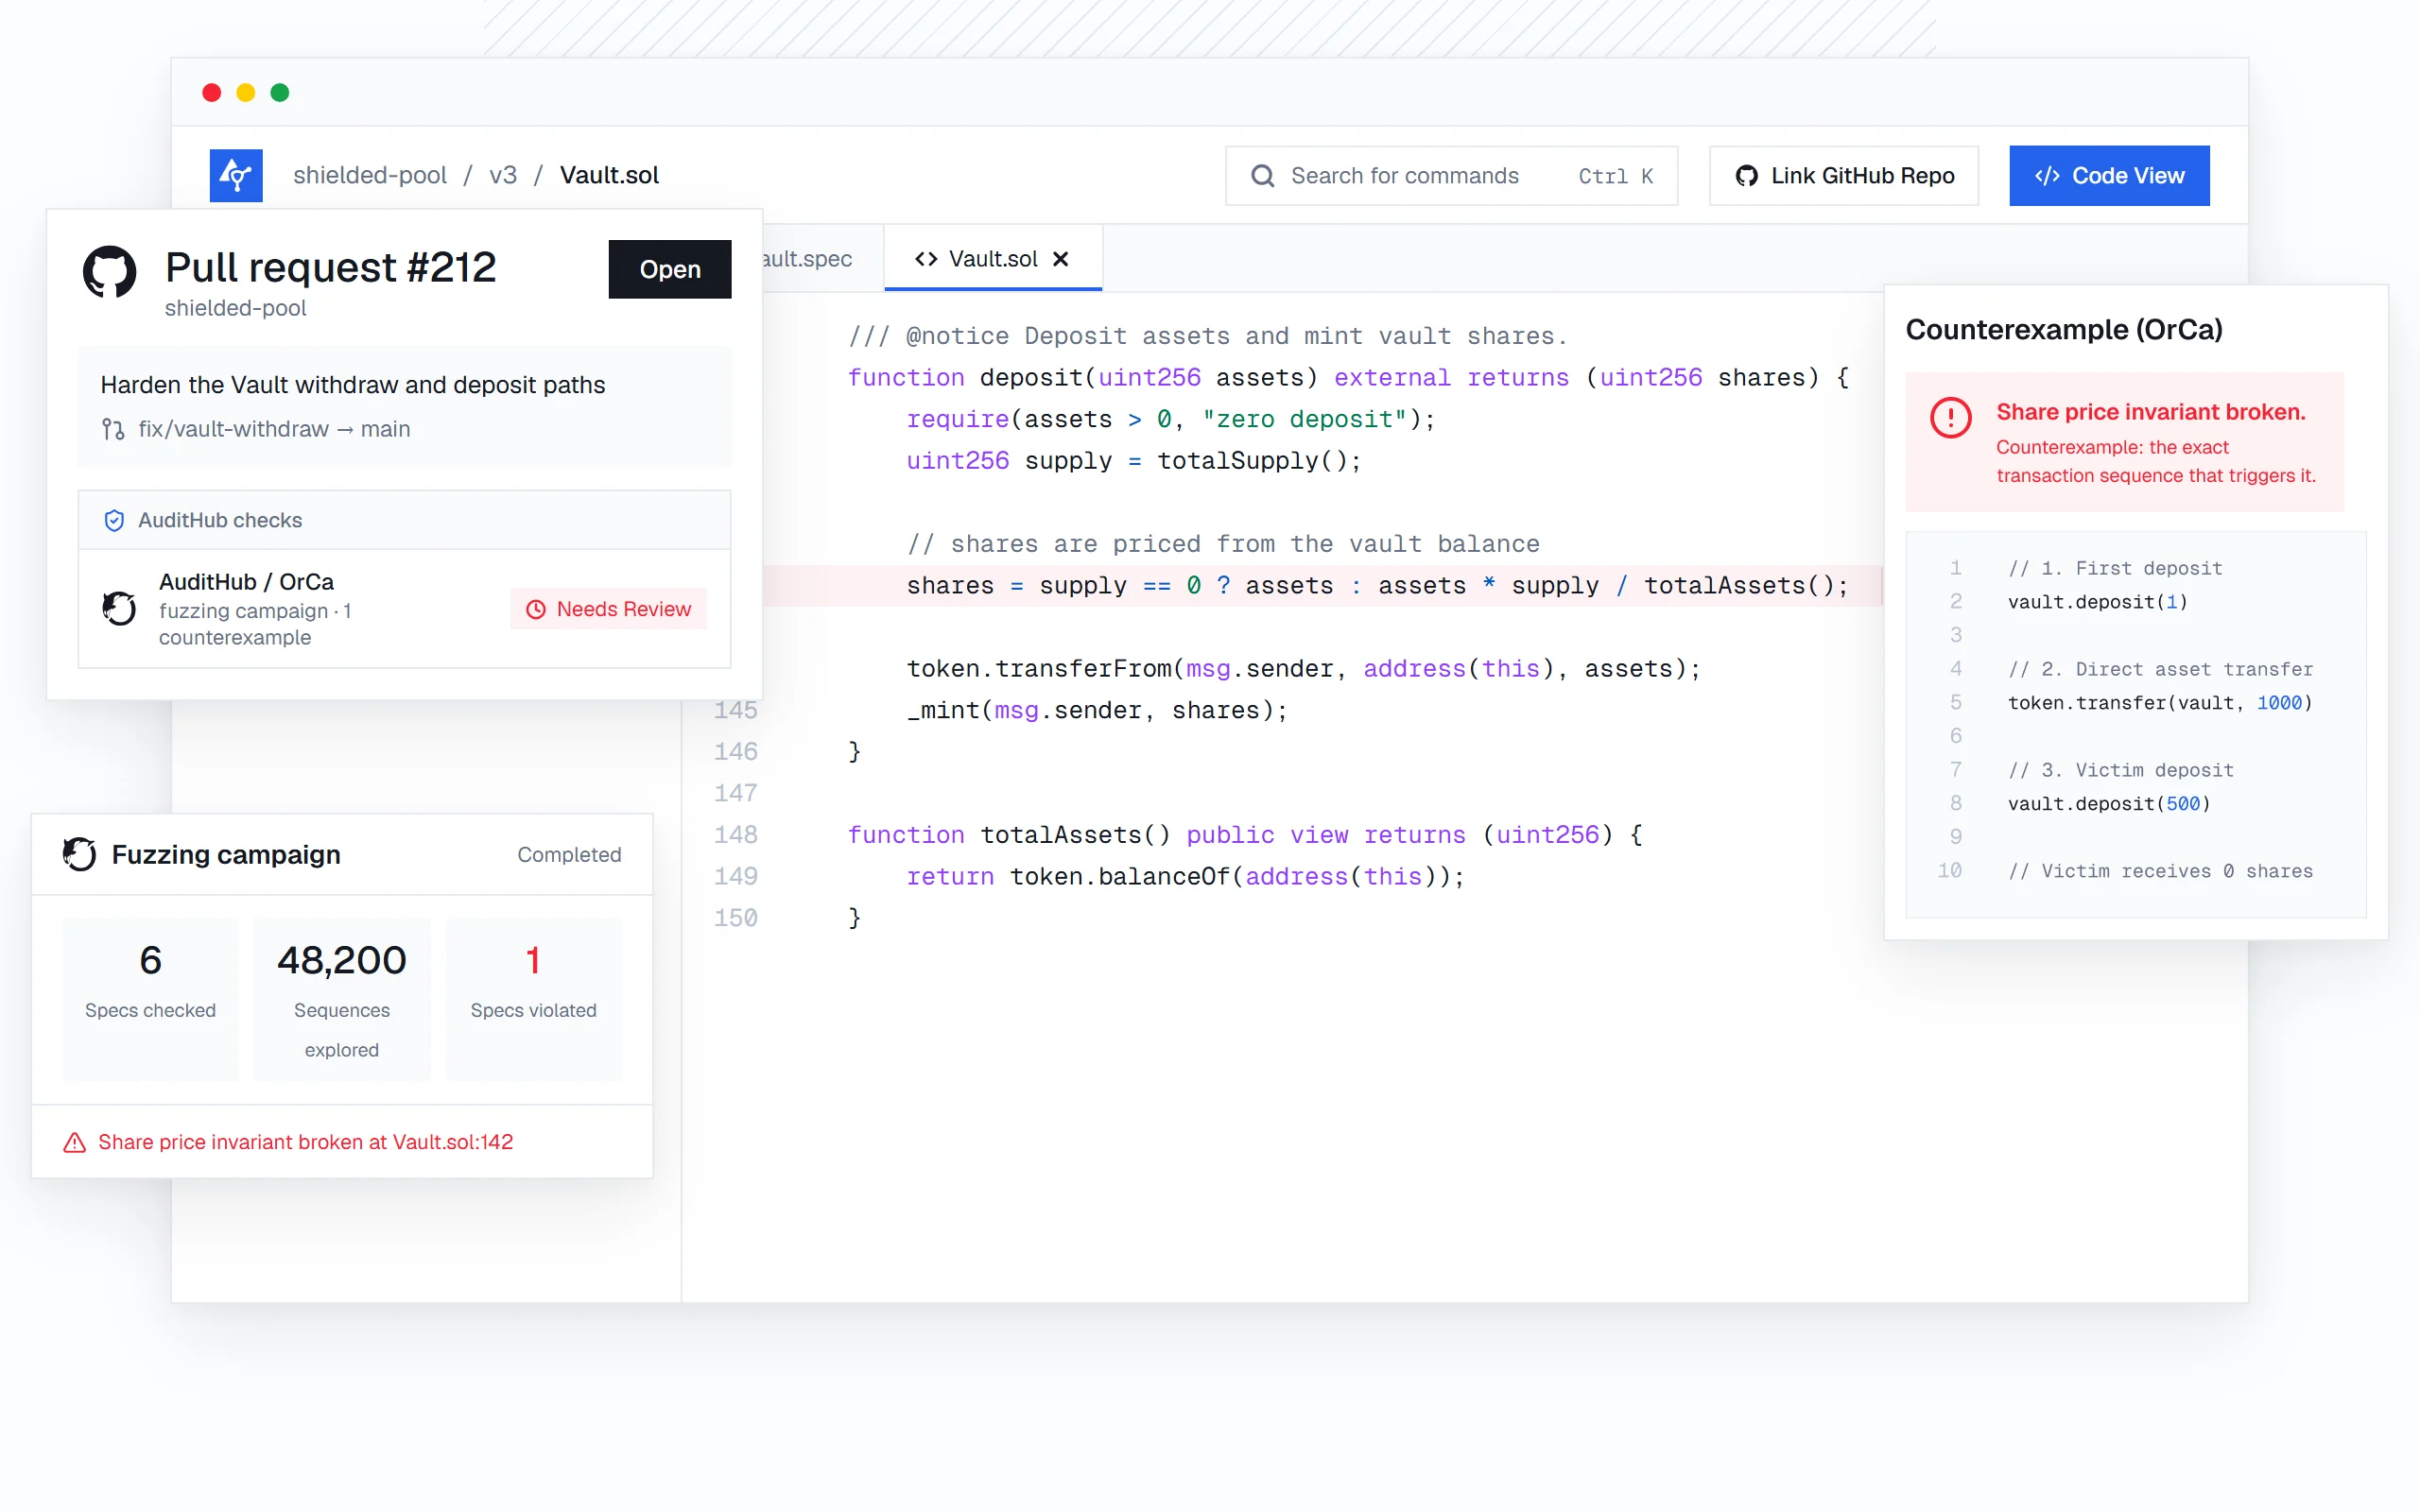
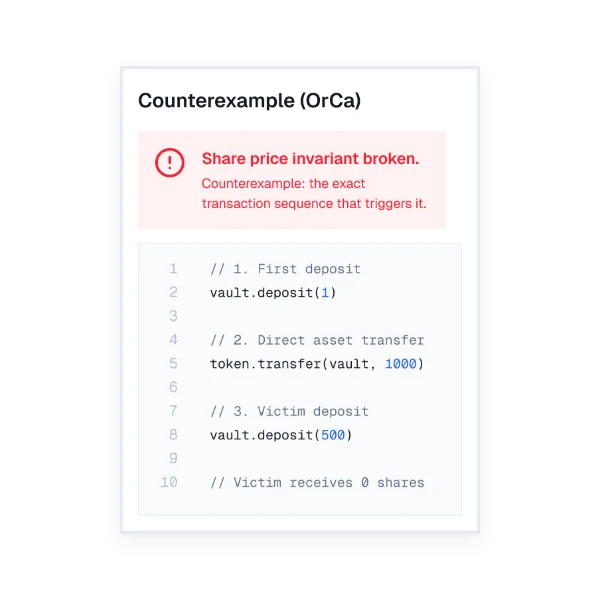
Vault.sol open in AuditHub with the share price computation flagged by OrCa: the counterexample that breaks the share price invariant, the fuzzing campaign statistics and the OrCa check on the pull request.

What OrCa tests in your smart contracts

OrCa tests your contracts against the behavior you describe, so a violation shows up even when nothing crashes.

// 001

Invariant violations

States your protocol must never reach, tested across thousands of generated transaction sequences.

// 002

Unintended behavior

Calls that succeed when your spec says they must not, even without a revert or a crash.

// 003

Cross-contract interactions

How your contracts behave when composed, not just in isolation.

// 004

Reentrancy exploits

Attacks OrCa builds itself through auxiliary contracts, with no change to your source code.

// 005

Common protocol bugs

Out-of-the-box checks from the specification library for common protocols.

// 006

Regressions

Behavior you already specified, retested every time your code changes.

How specification guided fuzzing works in OrCa

Most fuzzers throw random inputs and wait for a crash. OrCa is specification guided: it explores your contracts against the behavior you state and validates every run against it.

// 001

Write your specs

Describe the expected behavior in [V], or start from the specification library.

// 002

Run a fuzzing campaign

OrCa generates thousands of transaction sequences on your Foundry or Hardhat project.

// 003

Review counterexamples

Each violation comes back with the exact inputs and the transaction trace, in [V] syntax.

From AI finding to a reproducible fuzzing trace

Scout flags a suspicious transaction sequence in your protocol. OrCa tests it against your spec and returns the evidence: the exact inputs and the trace that break the expected behavior.

Scout AI - Findings

MediumNeeds Review

Line 142

First depositor can inflate the share price

Vault.sol:142
agent-findingcontracts/Vault.sol

OrCa - Evidence

Invariant violated

Share price manipulation reproduced

The exact inputs and the trace that break the expected behavior.

Victim deposit500assets
Shares minted0

// COUNTEREXAMPLE FOUND

View transaction trace

Invariant testing with [V] specifications

A [V] spec states what must always or never happen, like a withdrawal that must never finish with a zero amount. Start from the specification library, and use OrCa hints for protocols that need specific inputs or setup.
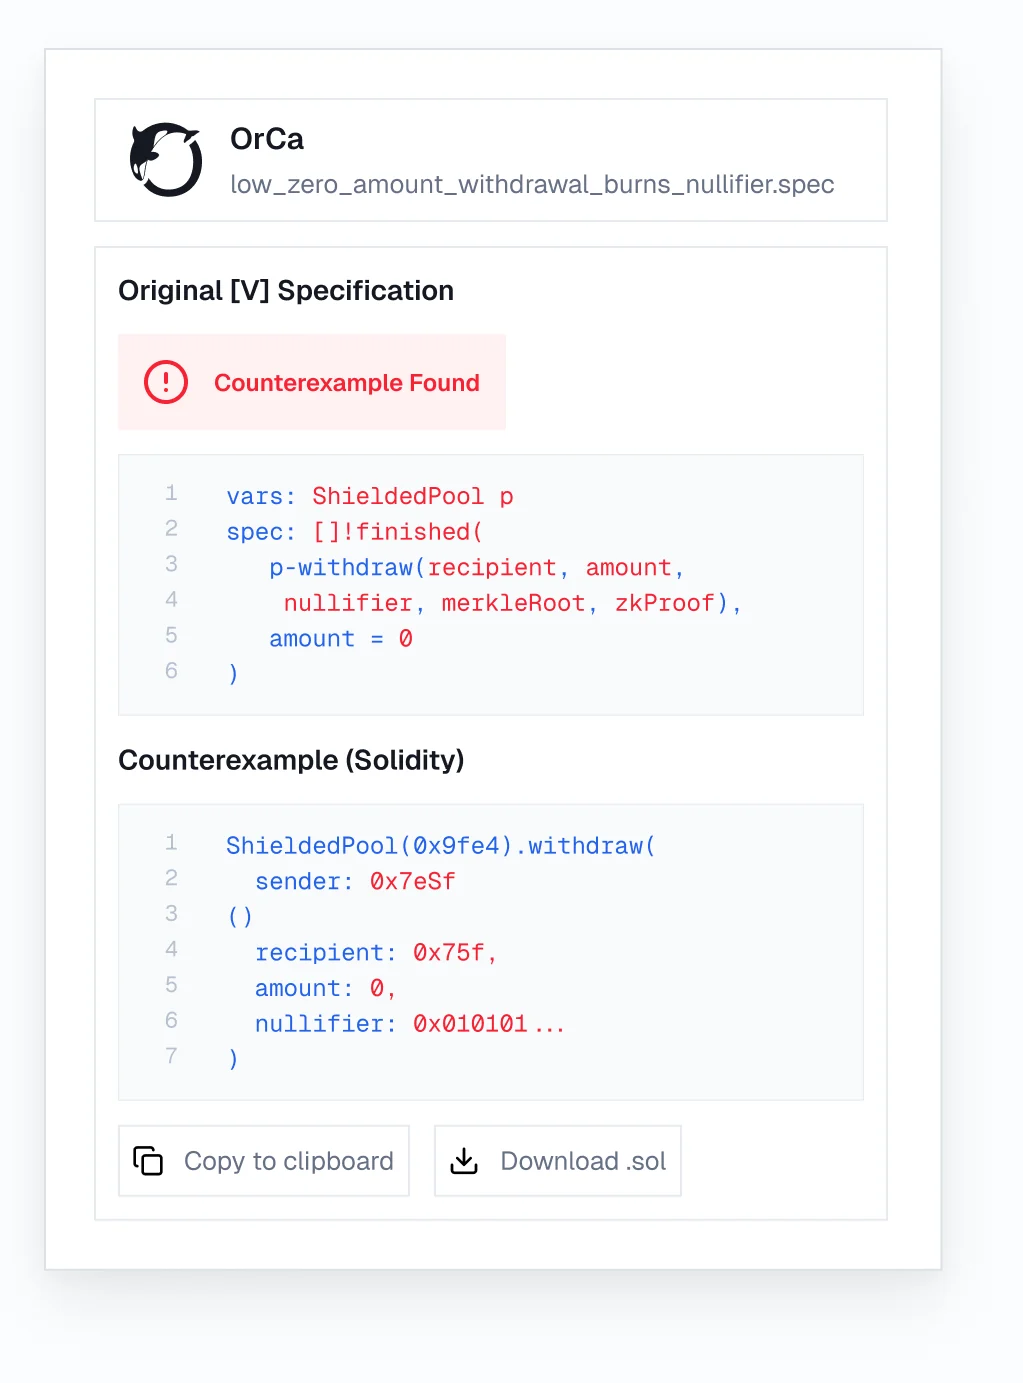
OrCa showing the original [V] specification, a withdrawal that must never finish with a zero amount, and the Solidity counterexample it found on the ShieldedPool demo contract.
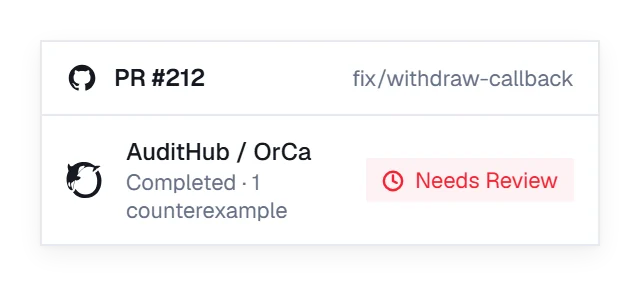
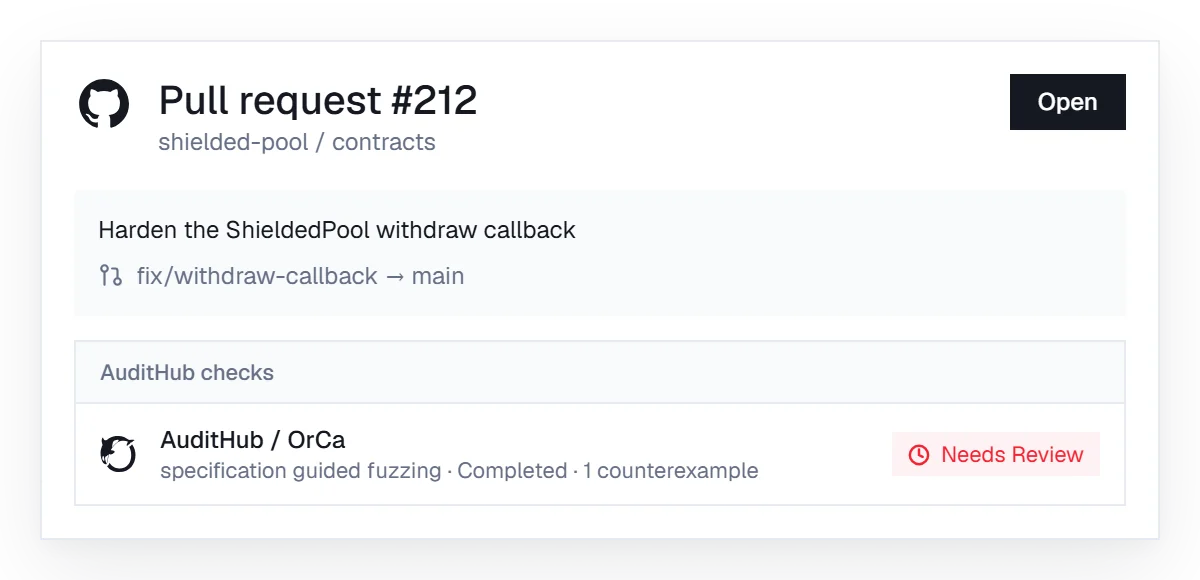
Pull request with the AuditHub OrCa check: completed, needs review.

Smart contract fuzzing in GitHub Actions, on every commit

OrCa works with Foundry and Hardhat projects and runs in your CI. Add a spec when your code changes, and every campaign retests what you already covered.

Working with a coding agent? Run OrCa from your session through AuditHub MCP.

Static analysis first, specification guided fuzzing second

Vanguard runs first, for breadth, and detects unsafe patterns across contract boundaries. OrCa follows and tests whether your contracts honor the behavior you specify, returning failing inputs when they do not.

Static analysis

Detects unsafe patterns across contract boundaries, for breadth.

Specification guided fuzzing

Tests whether your contracts honor the behavior you specify.

Fuzzing alongside your smart contract audit

OrCa retests your specs on every change, and its statistics report shows your auditors how your components actually interact. The audit still gives you a signed expert review.

Before audit

During audit

After audit
OrCa // EVERY CHANGE
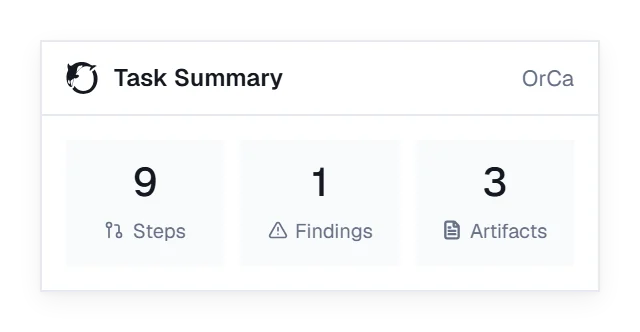
OrCa task summary on the demo project: steps, findings and artifacts.
AuditHub OrCa check on a pull request: completed, needs review.
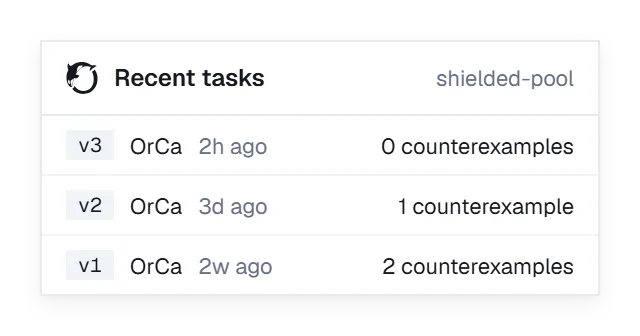
OrCa recent tasks across versions v1 to v3 of the demo project.

Smart contract fuzzer FAQ

What is a smart contract fuzzer?

A fuzzer generates large numbers of inputs and transaction sequences to exercise behavior your unit tests did not anticipate. OrCa is specification guided: it tests against the behavior you describe, not just for crashes.

Do I have to write the specifications myself?

You write specs in [V], a declarative language for what must always or never happen. You can also start from the specification library, which covers common protocols.

Which frameworks does OrCa support?

Foundry and Hardhat projects, Hardhat versions 2 and 3 included.

How long does a fuzzing campaign take?

Most campaigns run in 10 to 30 minutes.

How is OrCa different from formal verification?

OrCa tests your contracts against your specs with thousands of generated cases; it does not prove them. You get high-signal testing without the overhead of a proof.

Still have questions? Contact us

Learn more about smart contract fuzzing

Test your contracts against the behavior you intended

Run OrCa on your smart contracts today.