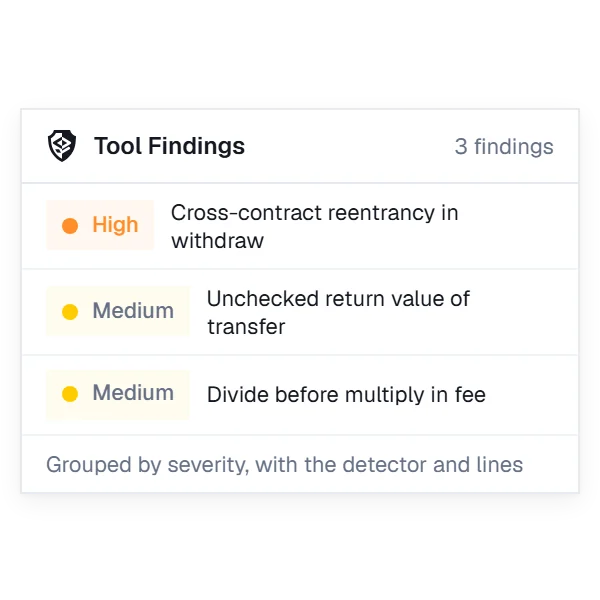
Smart contract static analysis that catches critical bugs before deployment

Vanguard detects reentrancy, access control issues and unsafe patterns, groups related findings, and runs in GitHub Actions.

For Solidity projects on Foundry or Hardhat.

Calibrated on 150+ security audits.
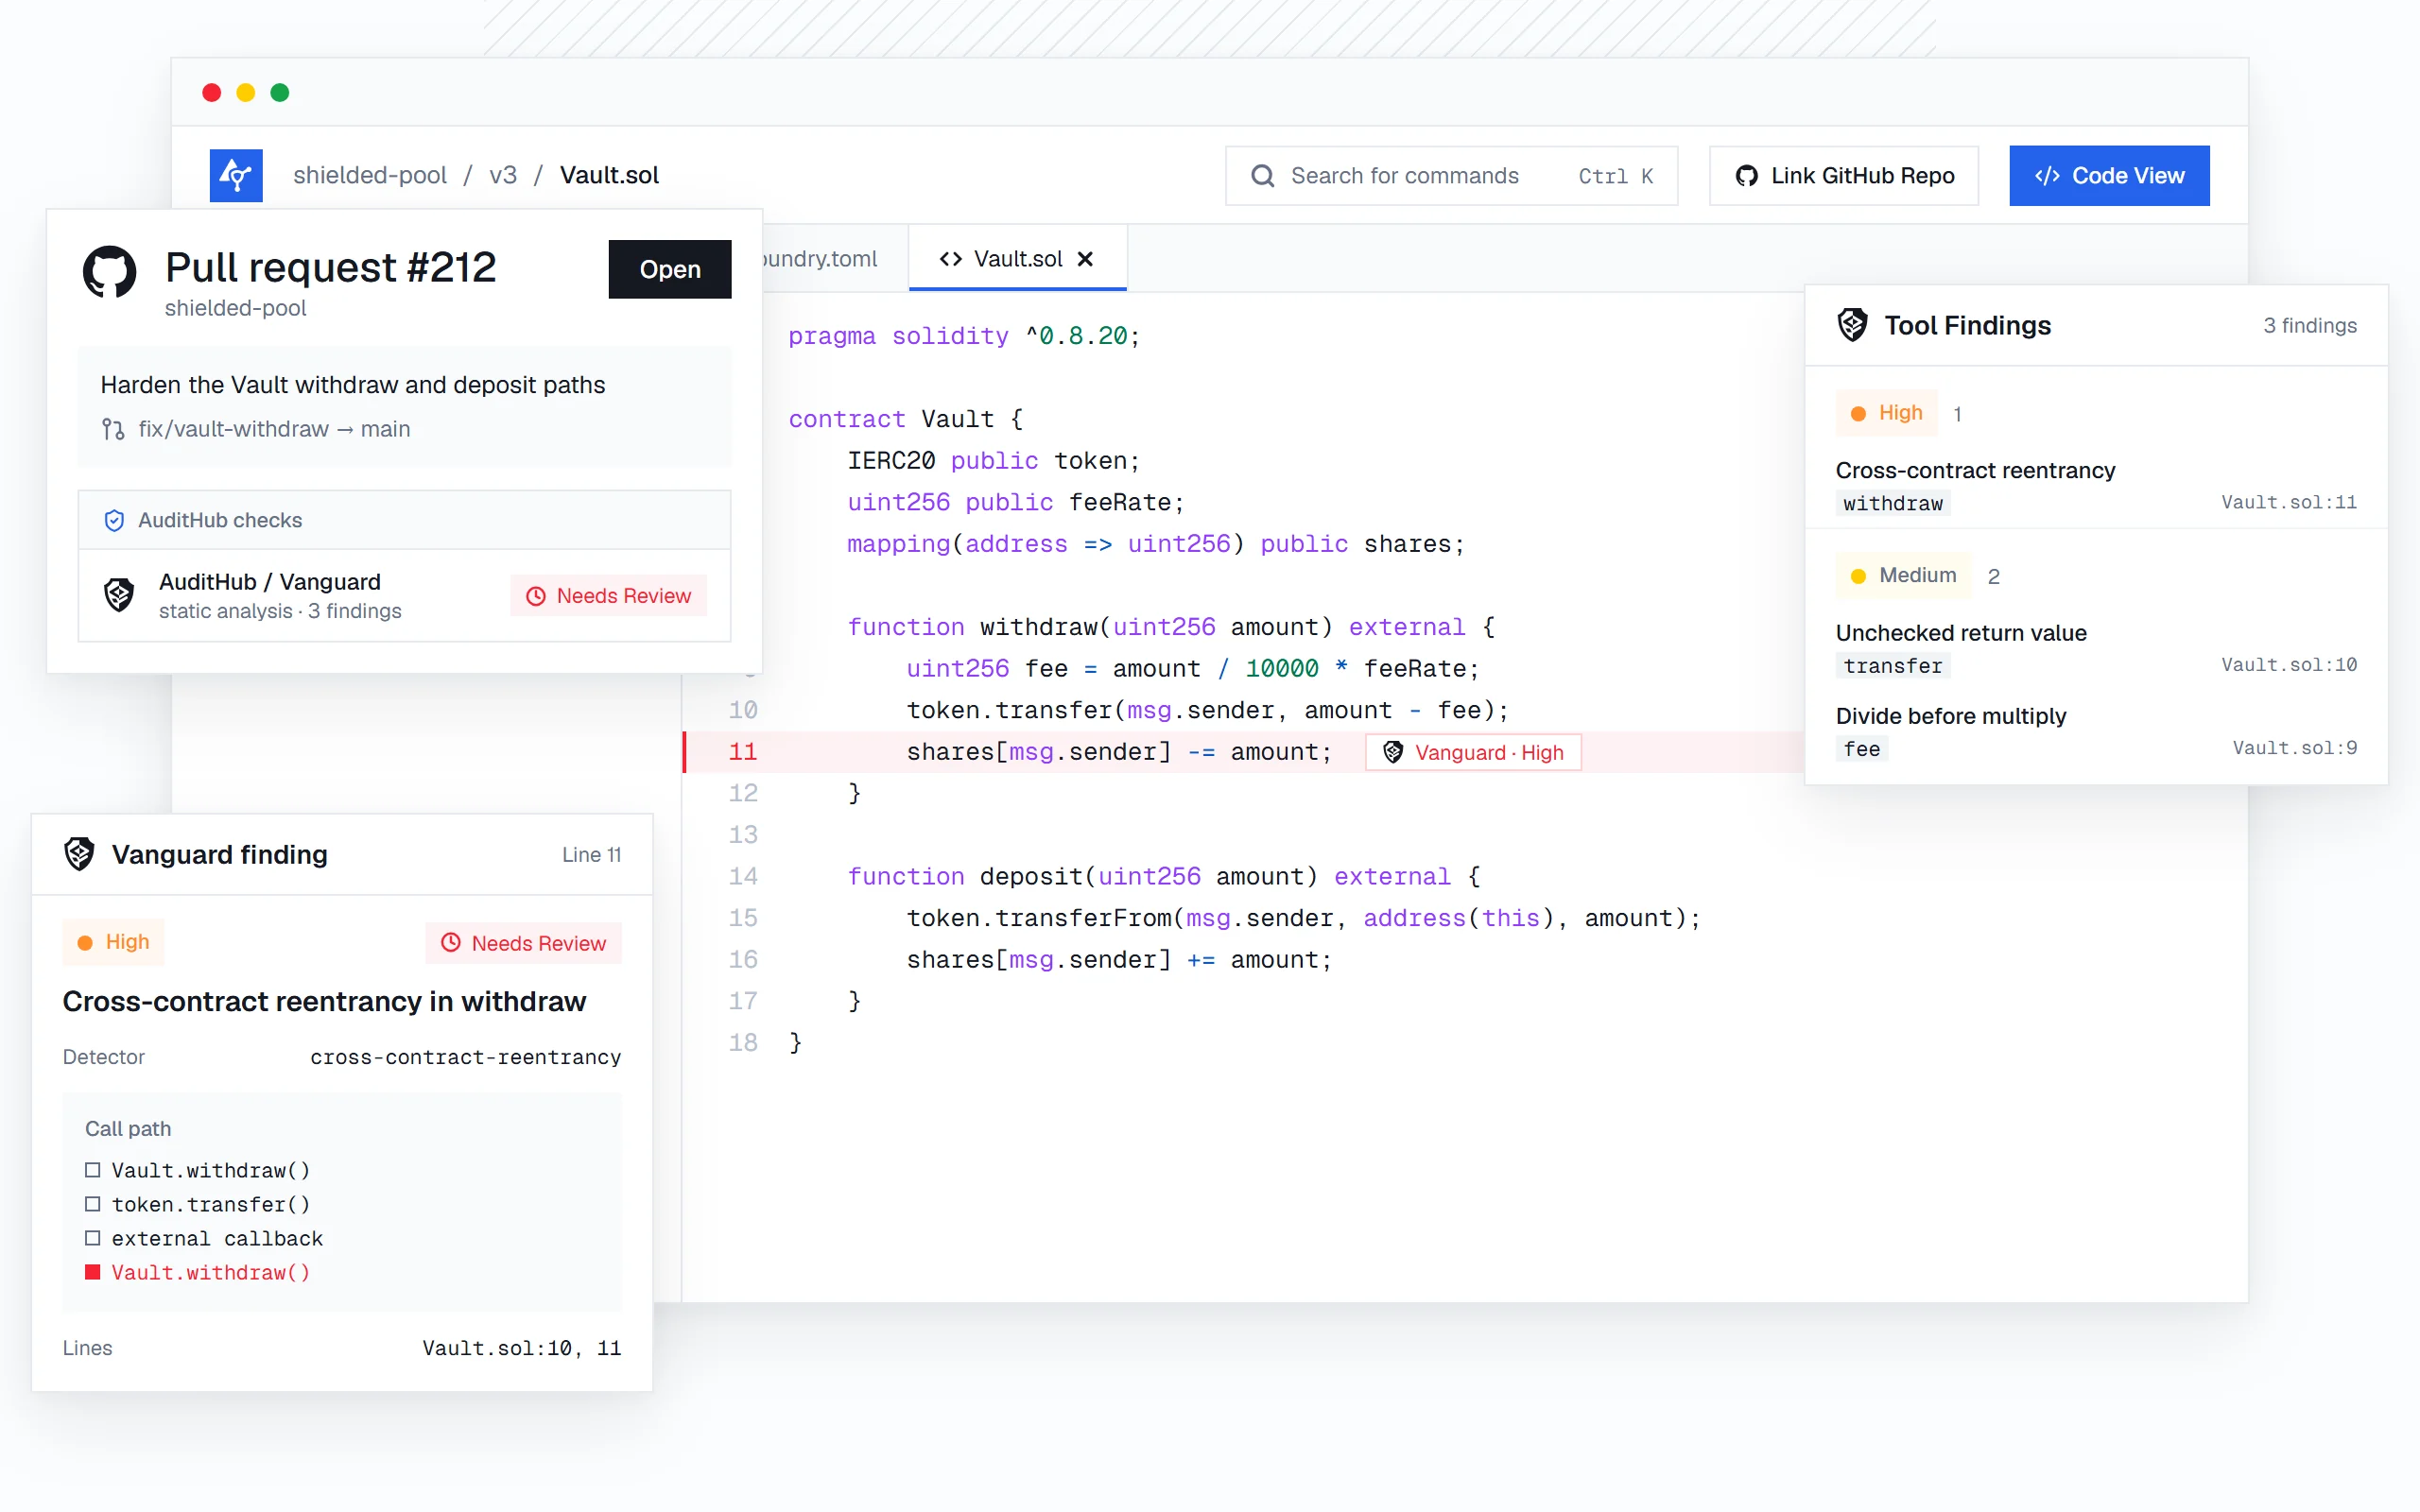
Vault.sol open in AuditHub with line 11 flagged by Vanguard: the Tool Findings grouped by severity, the cross-contract reentrancy finding with its call path, and the Vanguard check on the pull request.

What Vanguard detects in your Solidity code

Each built-in detector targets one vulnerability class and reasons about how your code behaves, not just how it reads.

// 001

Cross-contract reentrancy

Reentrancy across multiple contracts, including read-only reentrancy through shared storage.

// 002

Unchecked return values

External calls whose return values are never validated.

// 003

Divide before multiply

Precision loss caused by operator order.

// 004

Use before definition

Variables read before they are initialized.

// 005

Flash loan exposure

Logic an attacker can exploit within a single flash loan transaction.

// 006

Locked funds

Funds that can end up stuck inside a contract.

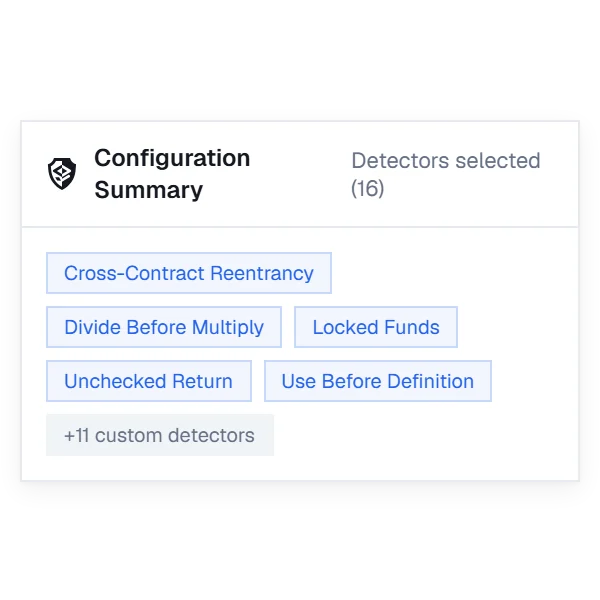
Plus 11 more built-in detectors, from missing or incorrect access control and low-level call hijacking to unsafe ERC20 approvals, ERC4626 checks and Uniswap callback validation, and custom detectors for your own patterns.

How smart contract static analysis works in Vanguard

Vanguard uses abstract interpretation to model your contracts. It follows calls and value across contract boundaries, so it understands interleaved transactions a pattern match would miss.

// 001

Connect your repository

Foundry or Hardhat, Solidity 0.8.4 and newer.

// 002

Run the analysis

Pick your detectors, Vanguard models every contract and call path.

// 003

Review grouped findings

Each report comes with call graphs, value flow and inferred access controls.
From AI finding to static analysis evidence

Scout flags a suspicious call path in your protocol. Vanguard checks it and returns the evidence: the call graph, the value flow and the exact lines involved.

Scout AI - Findings

HighNeeds Review

Line 11

Suspicious call path in withdraw

Vault.sol:11
agent-findingcontracts/Vault.sol

Vanguard - Evidence

Reentrancy detected

Cross-contract reentrancy detected

The call graph, the value flow and the exact lines involved.

Exact lines10, 11

// CROSS-CONTRACT REENTRANCY

View call graph

Custom detectors for your protocol's own risks

Write detectors in a concise query language, share them across your organization, or start from the standard library for ERC20, ERC4626 and Uniswap patterns. They run on the same engine and land in the same findings table.

-- custom detector definition
-- metadata: name, id, description, language
-- pattern: Program Analysis Query Language
-- engine: same as the built-in detectors
-- output: the same findings table
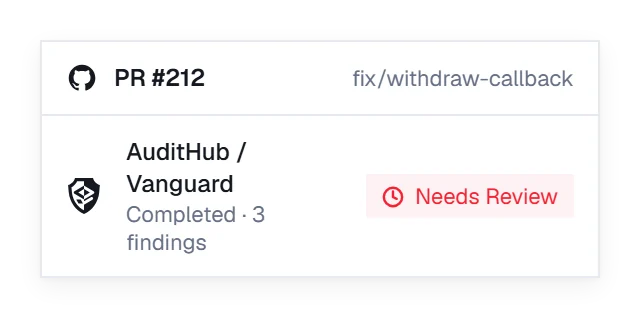
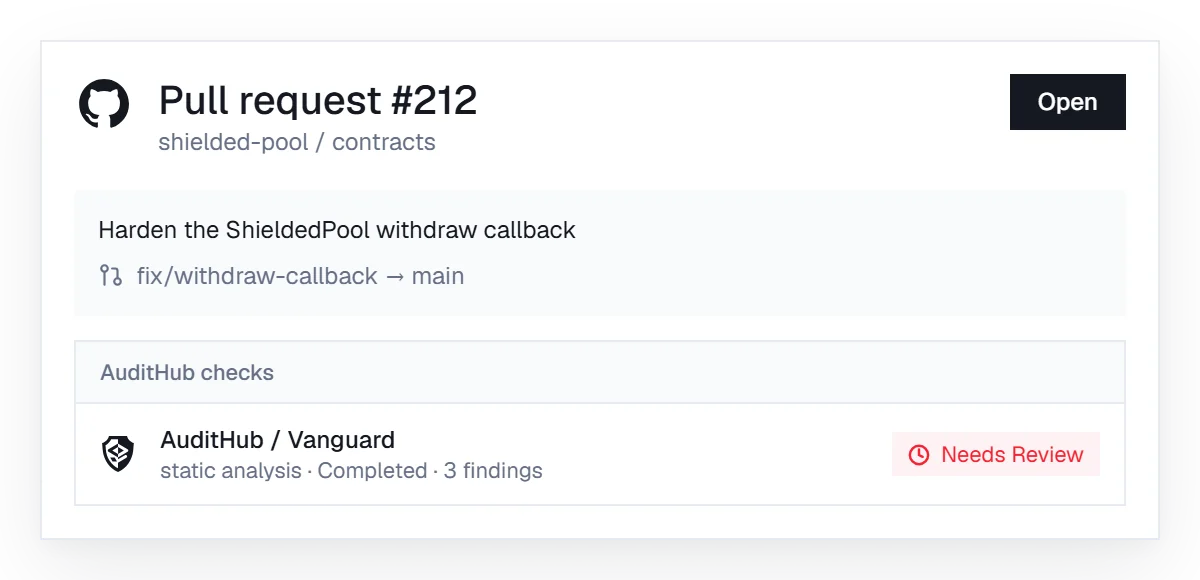
Pull request with the AuditHub Vanguard check: completed, needs review.

Static analysis in GitHub Actions, on every commit

Vanguard runs in your CI and reports during development, not after the fact. Mark a root cause once and every related false alarm clears in bulk.

Working with a coding agent? Run Vanguard from your session through AuditHub MCP.

Vanguard catches the suspects, OrCa tests the behavior

Vanguard runs first, for breadth. OrCa follows and fuzzes your contracts against the behavior you specify in [V], returning exact inputs and traces when a property fails.

Static analysis

Detects unsafe patterns across contract boundaries, for breadth.

Specification guided fuzzing

Tests whether your contracts honor the behavior you specify.

Static analysis alongside your smart contract audit

Vanguard checks your code continuously, so your auditors start on cleaner code and spend their time on design and logic. The audit still gives you a signed expert review.

Before audit

During audit

After audit
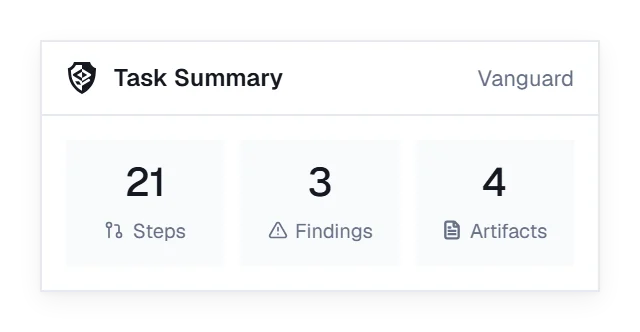
Vanguard // EVERY CHANGE
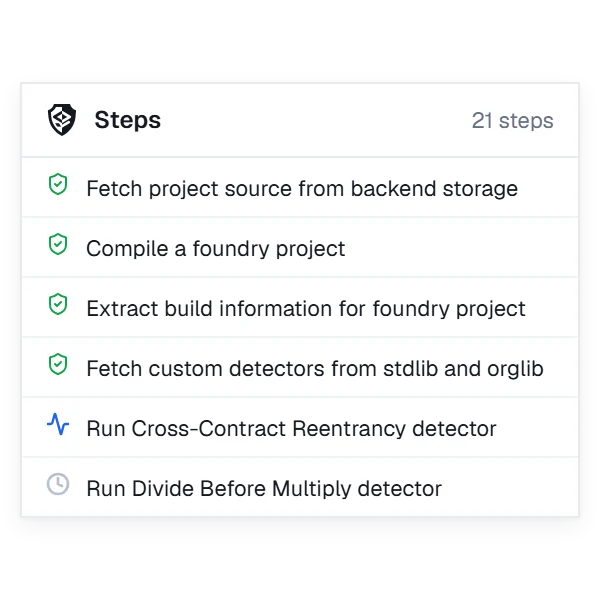
Vanguard task summary on the demo project: steps, findings and artifacts.
AuditHub Vanguard check on a pull request: completed, needs review.
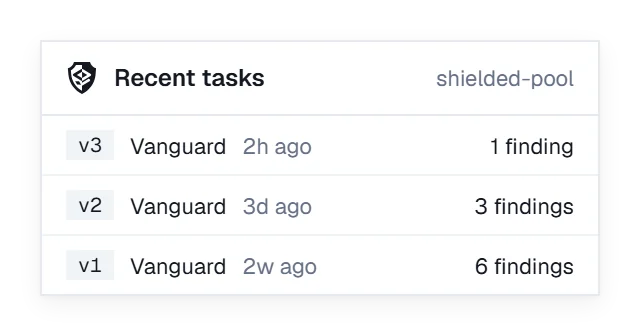
Vanguard recent tasks across versions v1 to v3 of the demo project.

Smart contract static analysis FAQ

What is smart contract static analysis?

It examines your contract code without executing it to find vulnerabilities before deployment. Vanguard goes further than pattern matching: it models how your contracts behave across calls.

Which Solidity versions and frameworks does Vanguard support?

Solidity 0.8.4 and newer, on Foundry and Hardhat projects.

How does Vanguard keep false positives low?

Its detectors are calibrated on 150+ security audits, related findings are grouped, and marking a root cause clears linked false alarms in bulk.

Can I write my own detectors?

Yes. Custom detectors use a concise query language and run on the same engine as the built-in ones.

Does Vanguard replace a smart contract audit?

No. It checks your code continuously between audits, and the audit gives you a signed expert review.

Still have questions? Contact us

Learn more about Solidity static analysis

Catch critical bugs before your next deployment

Run Vanguard on your Solidity code today.