Basic code reviewer
Reviews your code the way a human reviewer would, even on code that doesn't compile yet.
// BEST FOR EARLY BRANCHESScout reviews on the platform, AuditHub MCP works inside your own coding agent, and formal methods tools test the findings, so you act on evidence, not on a model's guess.
TRUSTED BY
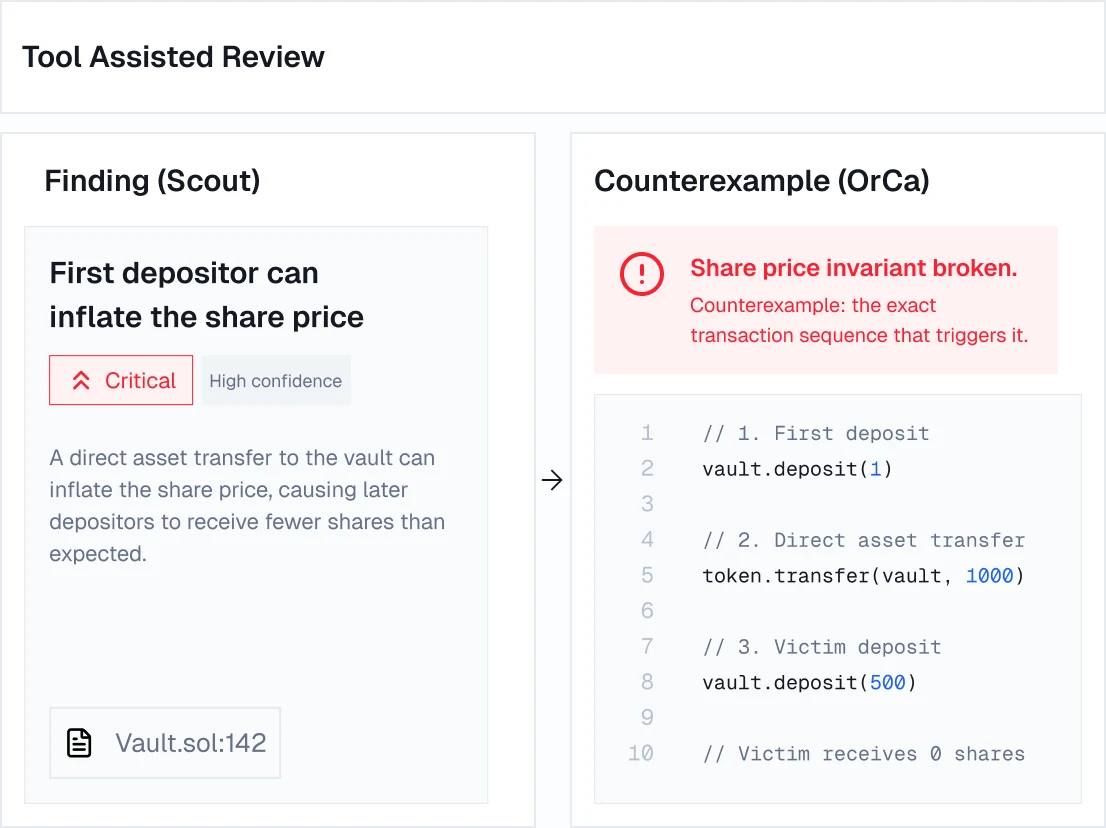
Scout reviews your code on the AuditHub platform, then tests each finding with the right security tool, so every finding comes with its evidence.
Meet Scout
Reviews your code the way a human reviewer would, even on code that doesn't compile yet.
// BEST FOR EARLY BRANCHES
Plans and runs Vanguard, OrCa, ZK Vanguard and Picus against its threat model. Each finding comes with a location, severity, confidence score and the tool output, including counterexamples.
// BEST FOR AUDITS AND RELEASESScout keeps the threat model and your corrections between runs, so your credits go to new code, not to relearning the old.
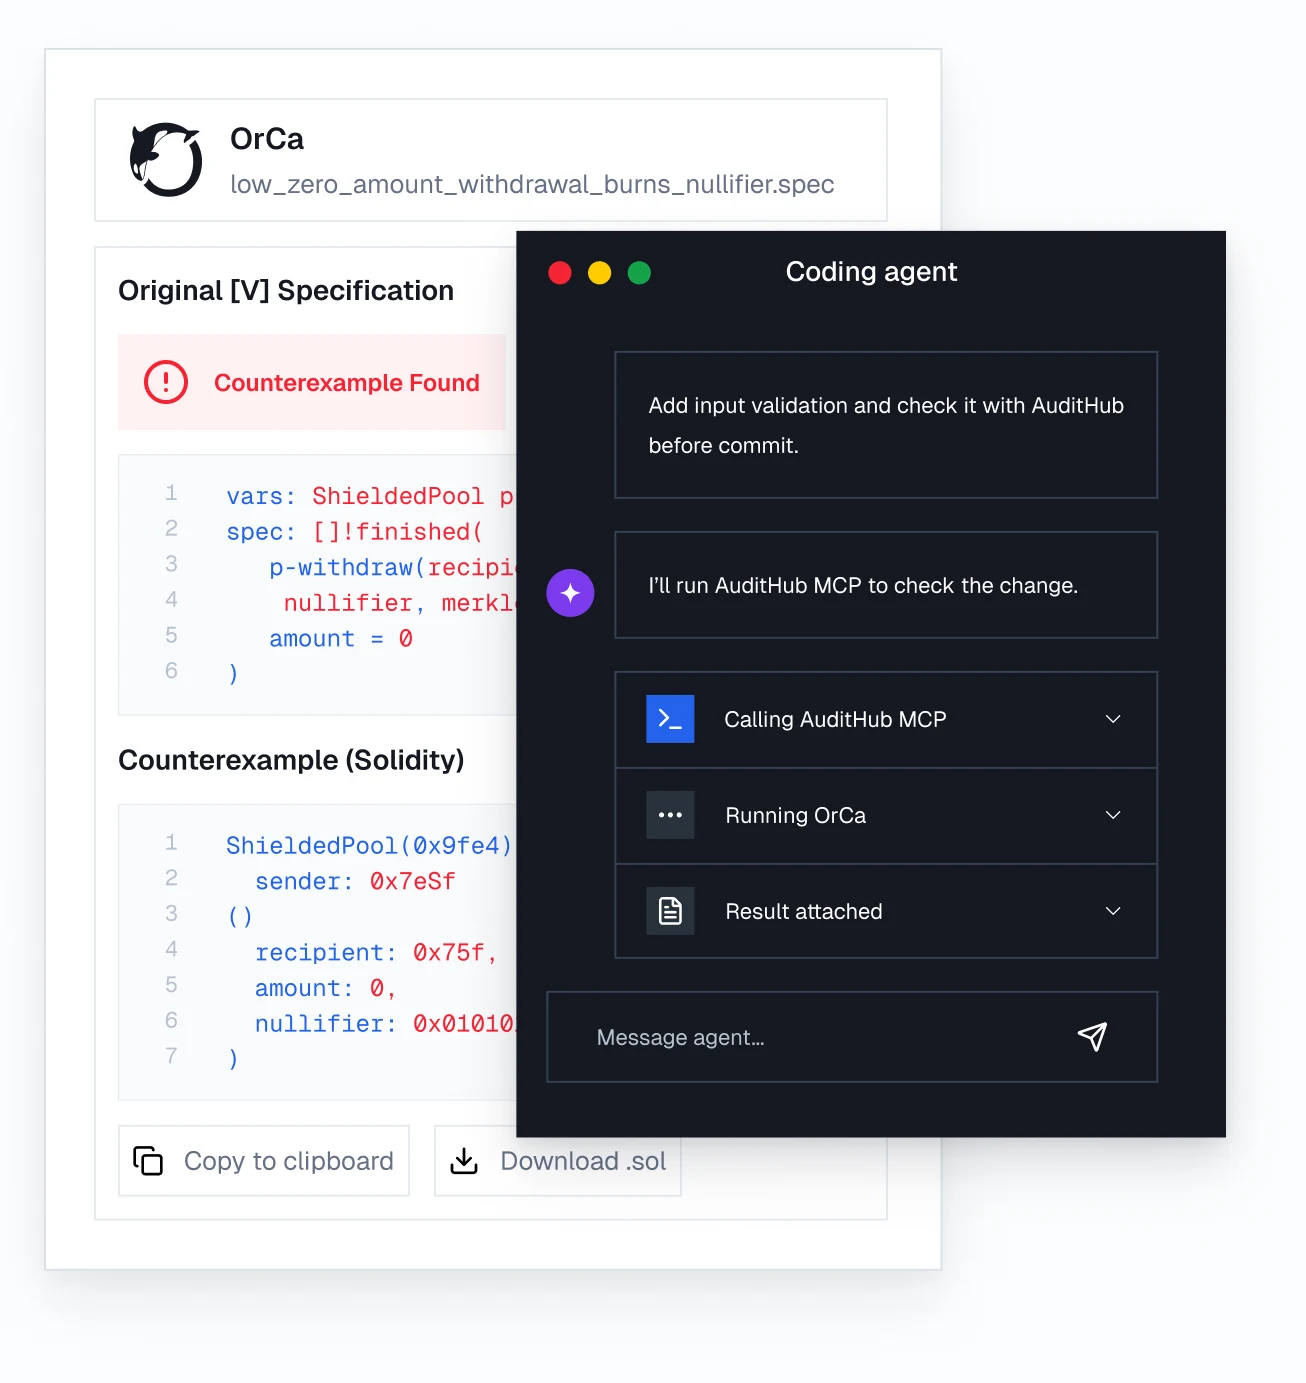
AuditHub MCP lets your coding agent call the security tools during the session, so the code it writes is checked before you commit it.
AuditHub MCP works inside the agent you already use.
The server is open source, so you can check every call it makes.
Every security tool is available from the Free plan.
Start for Free NowSign up with GitHub or Google.
Create your account
Get started with AI code security in minutes.
Continue with GitHub Continue with Googleor
Password
Create a password Create accountOr install AuditHub MCP in your coding agent.
Connect a repository
Select a source to start scanning for security issues.
Git repository AuditHub MCPRepository URL
https://github.com/acme/web-appBranch or revision
main Connect repositoryWith the evidence behind them.
11 findings
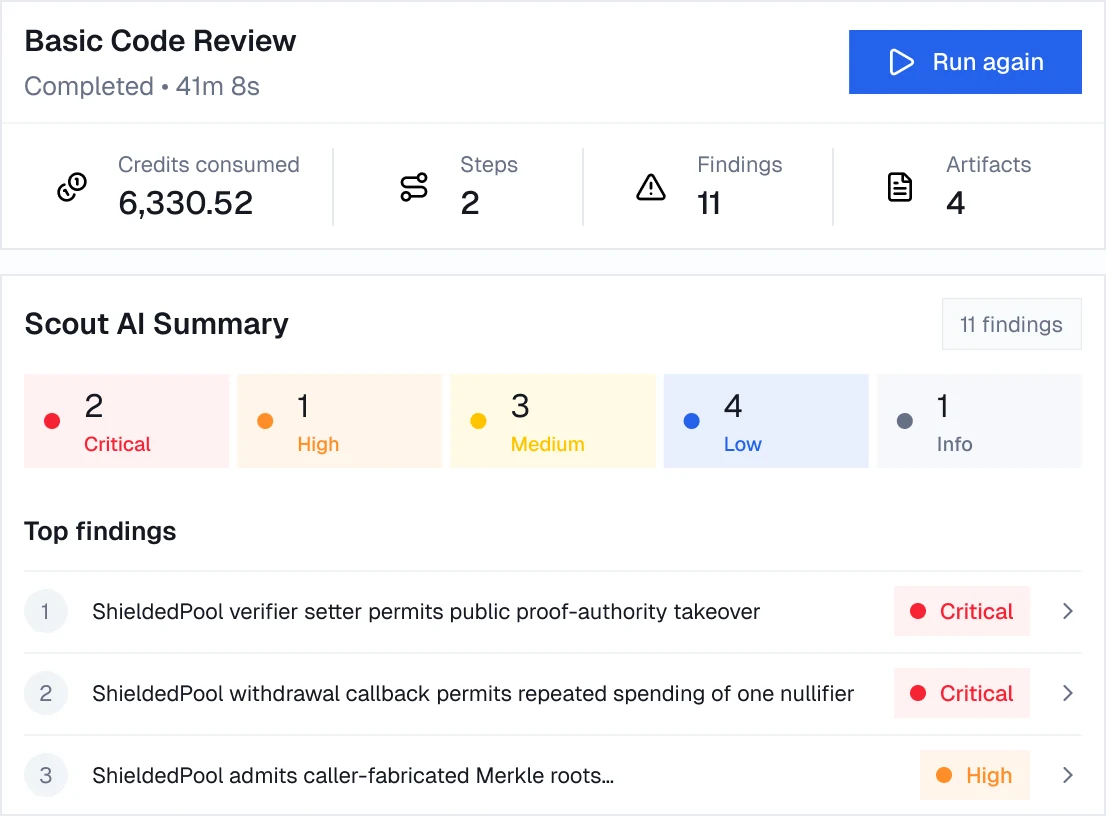
11 confirmed findings from the latest Scout review.
ShieldedPool verifier setter permits public proof-authority takeover
Line 108ShieldedPool withdrawal callback permits repeated spending of one nullifier
Line 52ShieldedPool admits caller-fabricated Merkle roots without authenticating an a...
Line 35You stay in control of your code, your spend and your results, whichever route you use.
Read our Trust pageThe server is open source.
Scout stops at the credit budget you set and keeps every finding it made.
Download report.md and findings.json from each run.
Your code never trains a model, ours or the model providers'.
Everything you need to know about Scout, how it reviews your code, uses security tools, manages credits, and fits into your security workflow.
AI agents review your code for vulnerabilities. On AuditHub, security tools built on formal methods check what the agents find, so you act on evidence, not on a model's guess.
Yes. Every security tool is available from the Free plan. Plans and credits are detailed on the Pricing page.
Use AuditHub MCP to check code while your coding agent writes it. Use Scout for a full review of your protocol before an audit or a release. You can use both.
Yes. ZK Vanguard catches likely underconstrained signals; Picus proves their absence.
No. AuditHub checks your code as you build, so your audit starts from a higher baseline. The audit still gives you a signed expert review.
Still have questions? Contact us
Run Scout on your protocol, or bring the security tools into your coding agent.