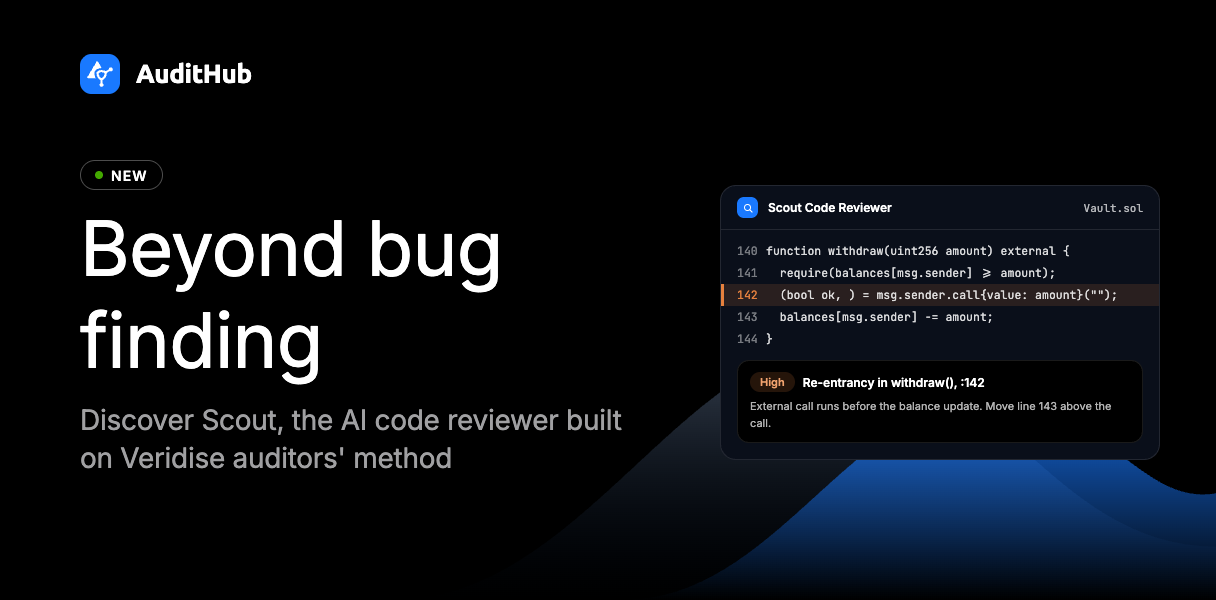
Scout maps your system’s threats and ranks every finding by severity, the way auditors review code. Built for teams shipping L1s, L2s, bridges, oracles and proving systems.
Benefit from the Launch offer: 20,000 free credits, a $200 value.
AuditHub launches Scout, the AI code reviewer, made with clients, partners and security teams in mind.
In line with its mission to deliver security, not just find bugs, AuditHub puts Veridise auditors’ method in the hands of any team preparing an audit or reviewing changes between two audits.
AI agents have become good at finding bugs. Headlines keep reporting the critical issues they catch. But a list of bugs is not a secure system.
On L1s, L2s, bridges, oracles and proving systems, the costly failures rarely sit in a single line of code. They sit in the assumptions between components: between a bridge and its relayer, in a circuit constraint that looks complete but isn’t, on an upgrade path nobody checked again.
That’s why auditors don’t start by hunting bugs. They start by mapping the system and what can go wrong. Scout reviews your code the same way.
The AI code reviewer that works like an auditor
Scout is refined by Veridise auditors as new threats emerge, so each review reflects what auditors see in the field today.
It reads your code the way our auditors do: the system first, then the places where its parts meet. Point Scout at your code and it:
- maps your system and builds a threat model
- delivers a findings summary, ranked by severity
- reviews your code even before it compiles
You set a credit budget for each review, and you keep every finding even if the review stops early.
Free: Run Scout on your code today, and get your first findings!
Built by the team behind 150+ audits
Veridise has audited these systems, from L1s and L2s to ZK circuits. Many of you know that work first hand. Scout does not replace your security audit. It clears the groundwork, so your auditors start on the hard problems.
Try it on this week’s code, with $200 in credits on us
You don’t need to point Scout at your whole protocol to see what it does. Pick the module you changed this week and run your first review.
- Preparing a security audit? Run Scout before your auditors arrive, and walk in with the easy findings fixed.
- Shipping between audits? Run it on what changed since your last report.
Our launch offer includes 20,000 free credits, a $200 value: enough for a review of several thousand lines, or a few smaller ones.
No card, no sales call. Running a larger team?
Talk to us about a team plan.
What comes next
This first version paves the way for Scout Tool Assisted Reviewer, which will add persistent memory and run specialized security tools. It will then sort the findings for you, the way an auditor would. Launch is planned for early 2027.
Interested by the next version of scout?
Subscribe to our newsletter or follow AuditHub on X to hear first when the Tool Assisted Reviewer launches.